There are many different ways a threat actor can target a victim, the more you know about these attacks and how they are designed to work, the better you can protect the systems you own, and the data that resides within them.
Here you will find links about various types of cyber attacks, what they are, how they work, and what can be done to protect against them
-
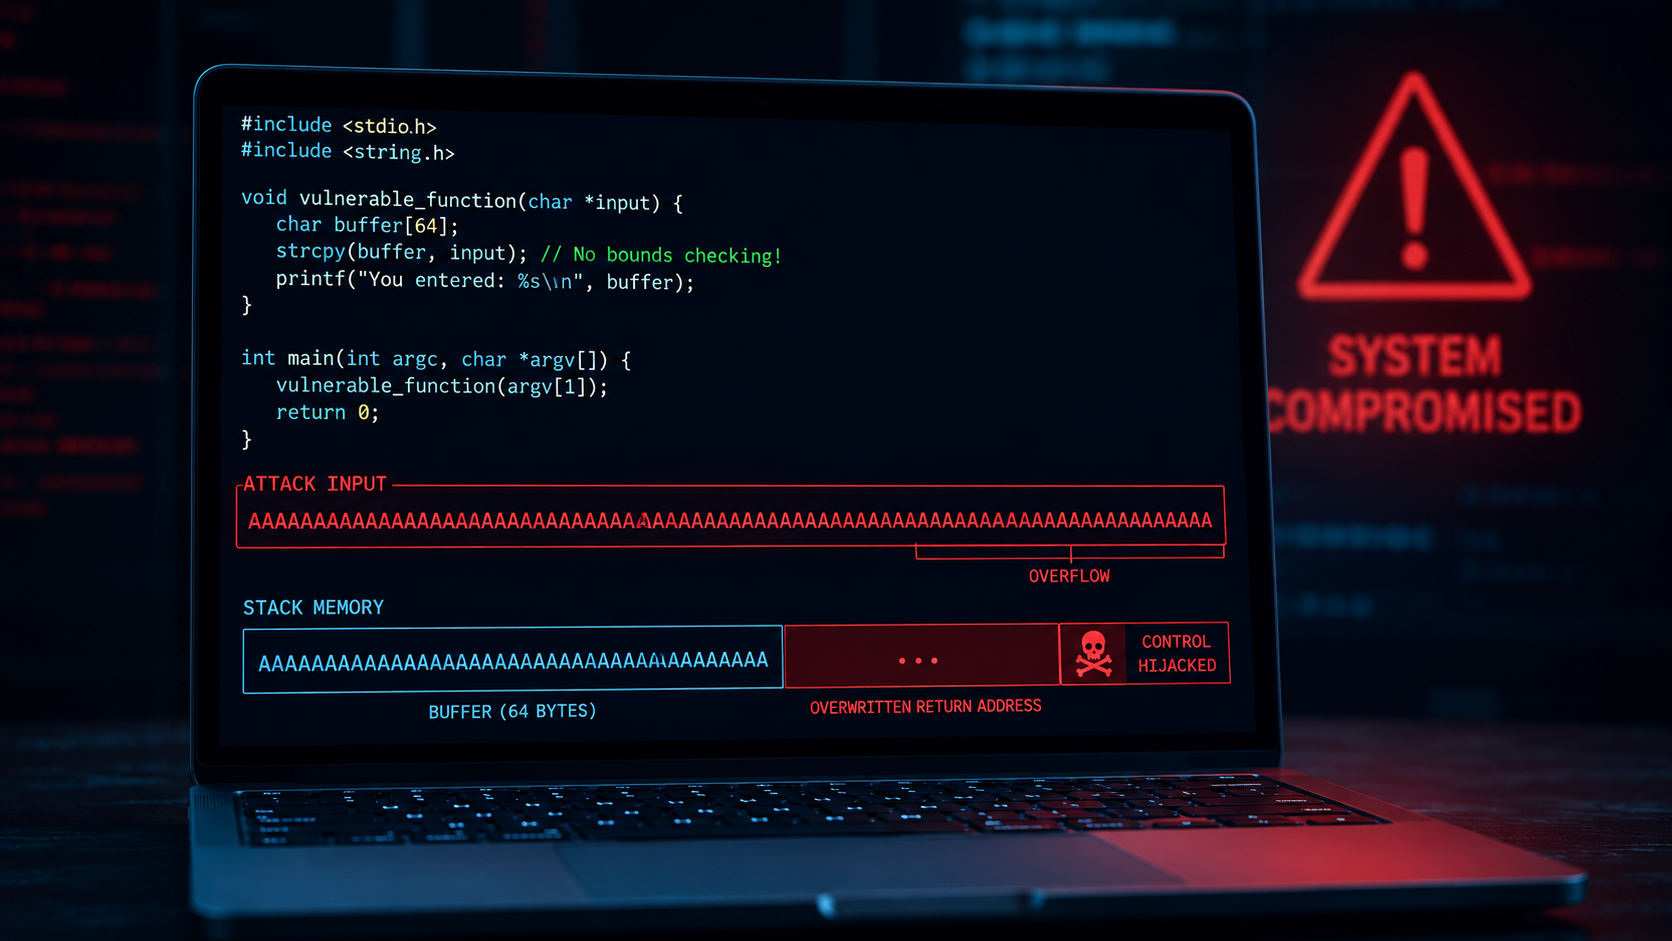 Buffer overflows
How overflowing a memory buffer lets an attacker run their own code.
-
 Denial of Service (DoS)
Flooding a system so legitimate users can’t get through.
-
 Distributed Denial of Service (DDoS)
Overwhelming a system with massive amounts of data.
-
 Botnets
Armies of hijacked devices working together on an attacker’s orders.
-
 Ransomware
Files locked, data held hostage, and a payment demand attached.
-
 Malware
The umbrella term for software built to damage or exploit a system.
-
 Phishing
Tricking someone into handing over credentials or clicking something they shouldn’t.
-
 Password attacks
Guessing, cracking, or stealing the keys to an account.
-
 Injection Attacks
Slipping malicious input into a system that trusted it too much.
-
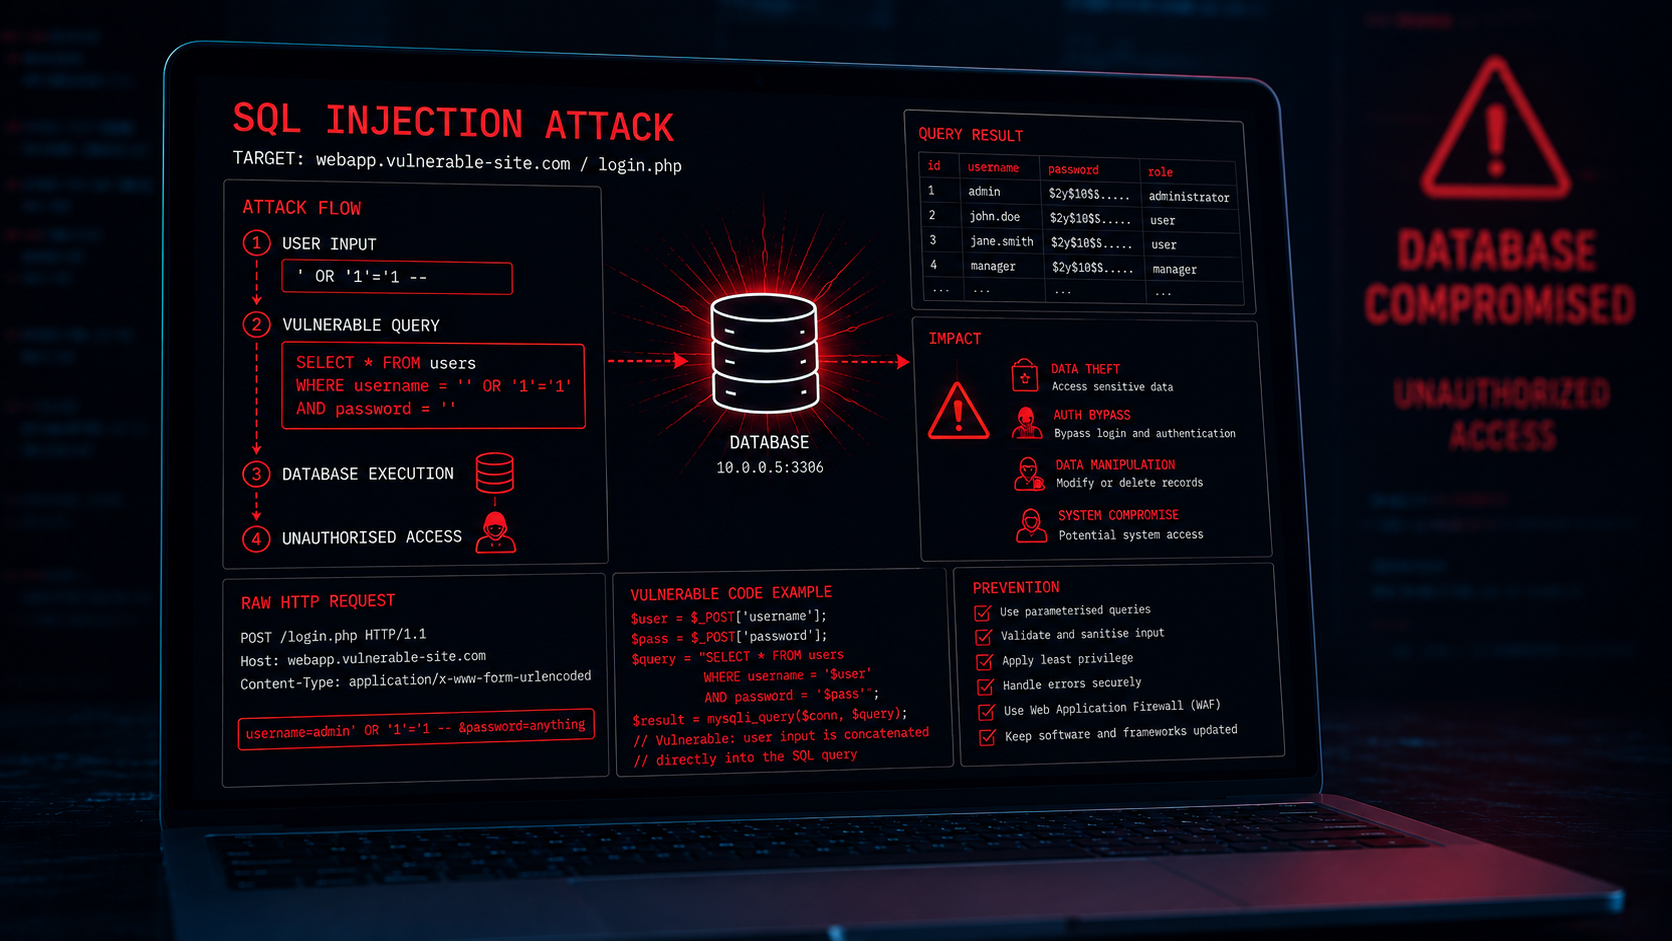 SQL Injection Attacks
Attacking databases through malicious input
-
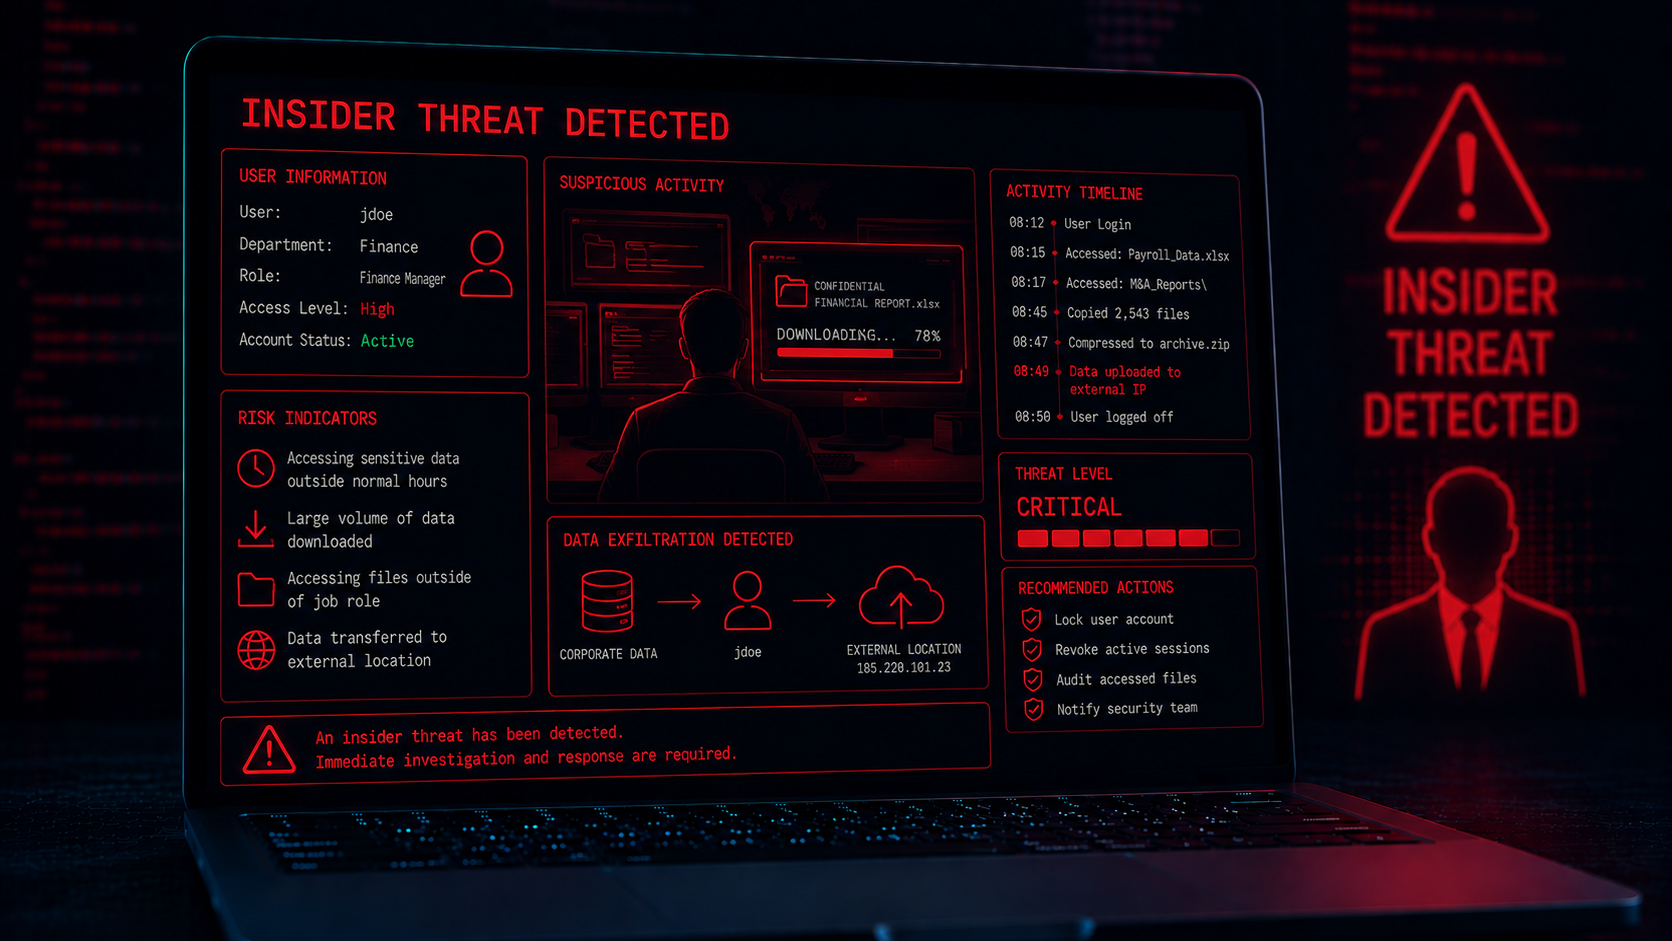 Insider threats
When the risk to a system comes from inside the organisation.
-
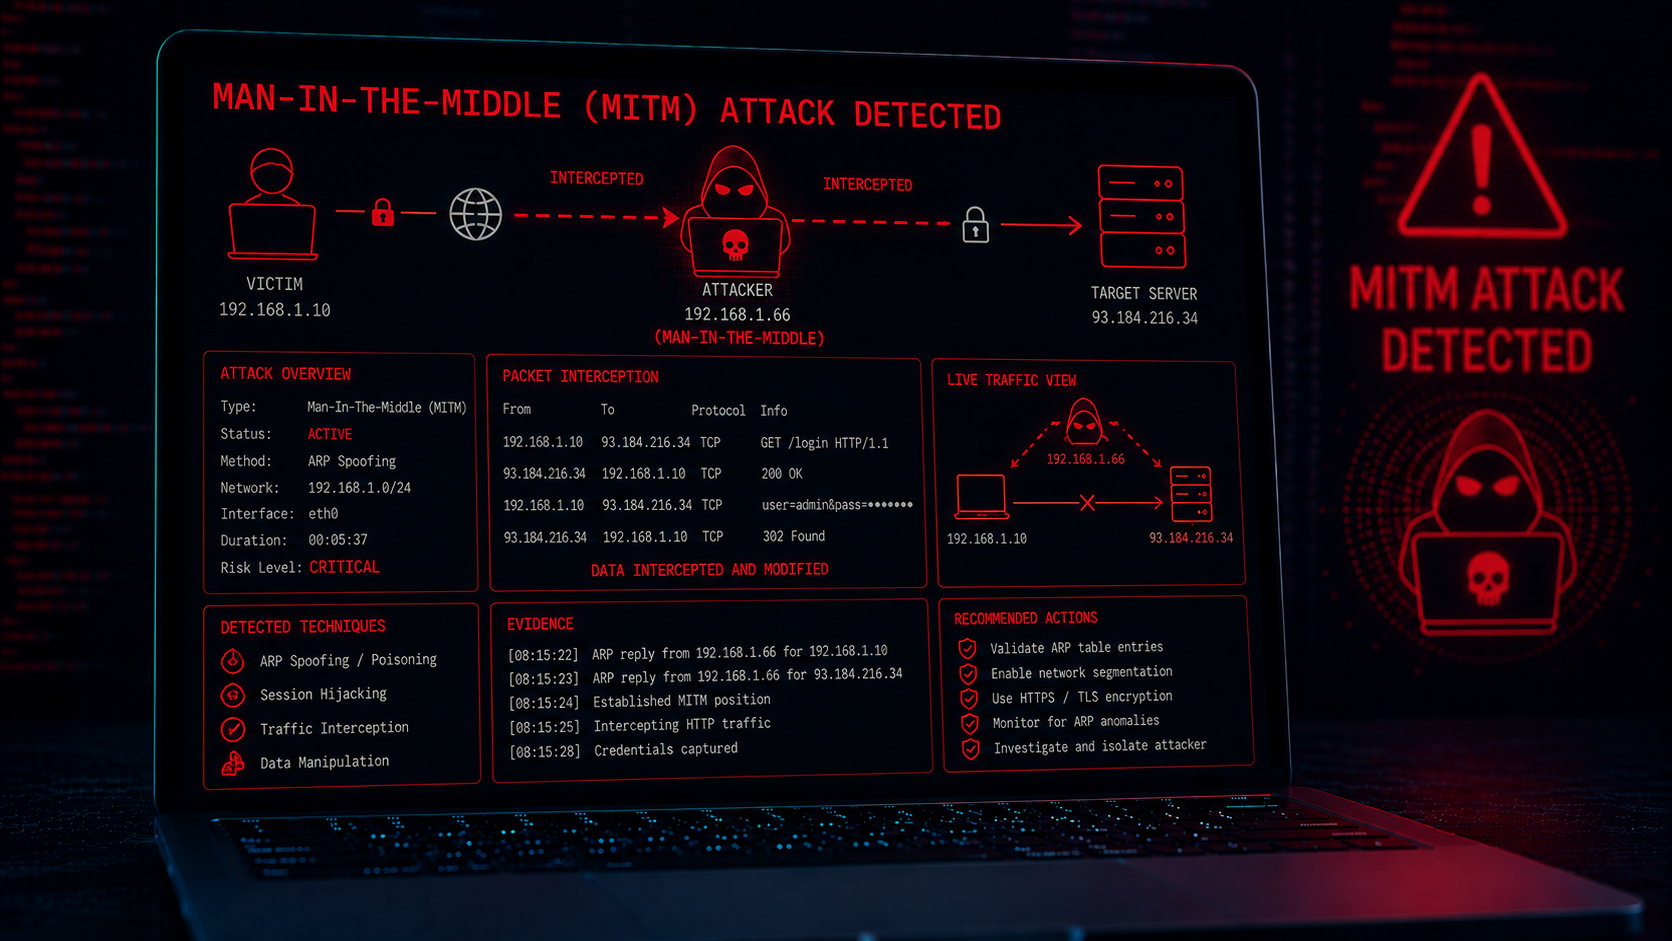 Man in the Middle (MiTM)
An attacker quietly sitting between two parties who think they’re talking directly.
-
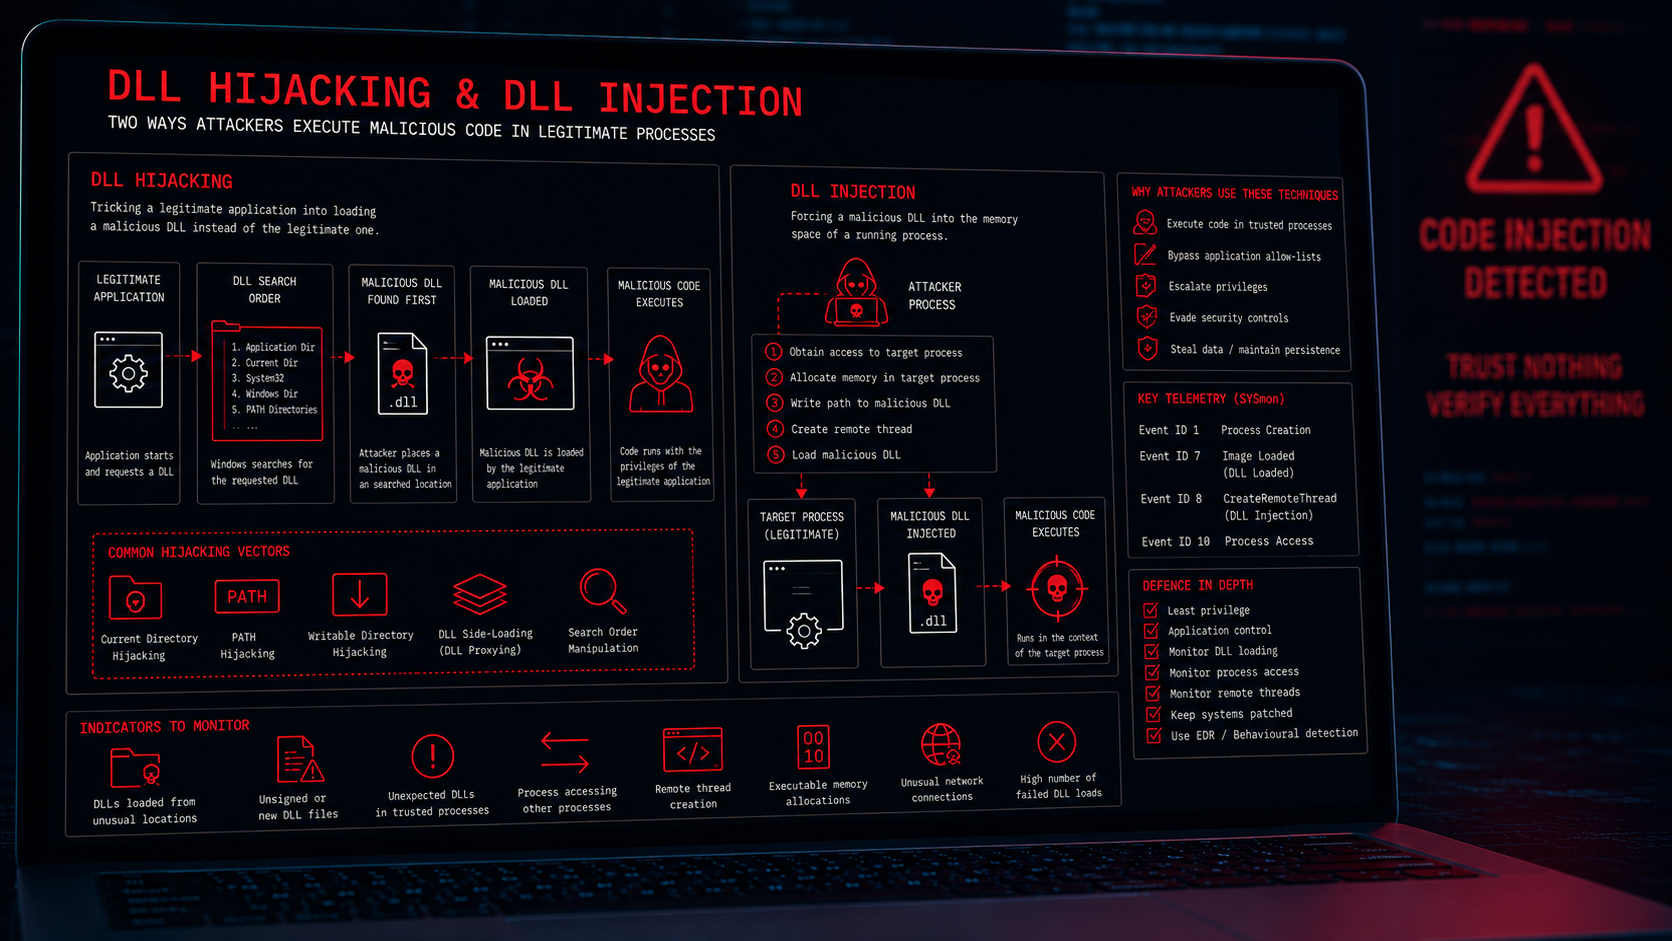 DLL Injection & Hijacking Attacks
Executing malicious code inside legitimate processes
-
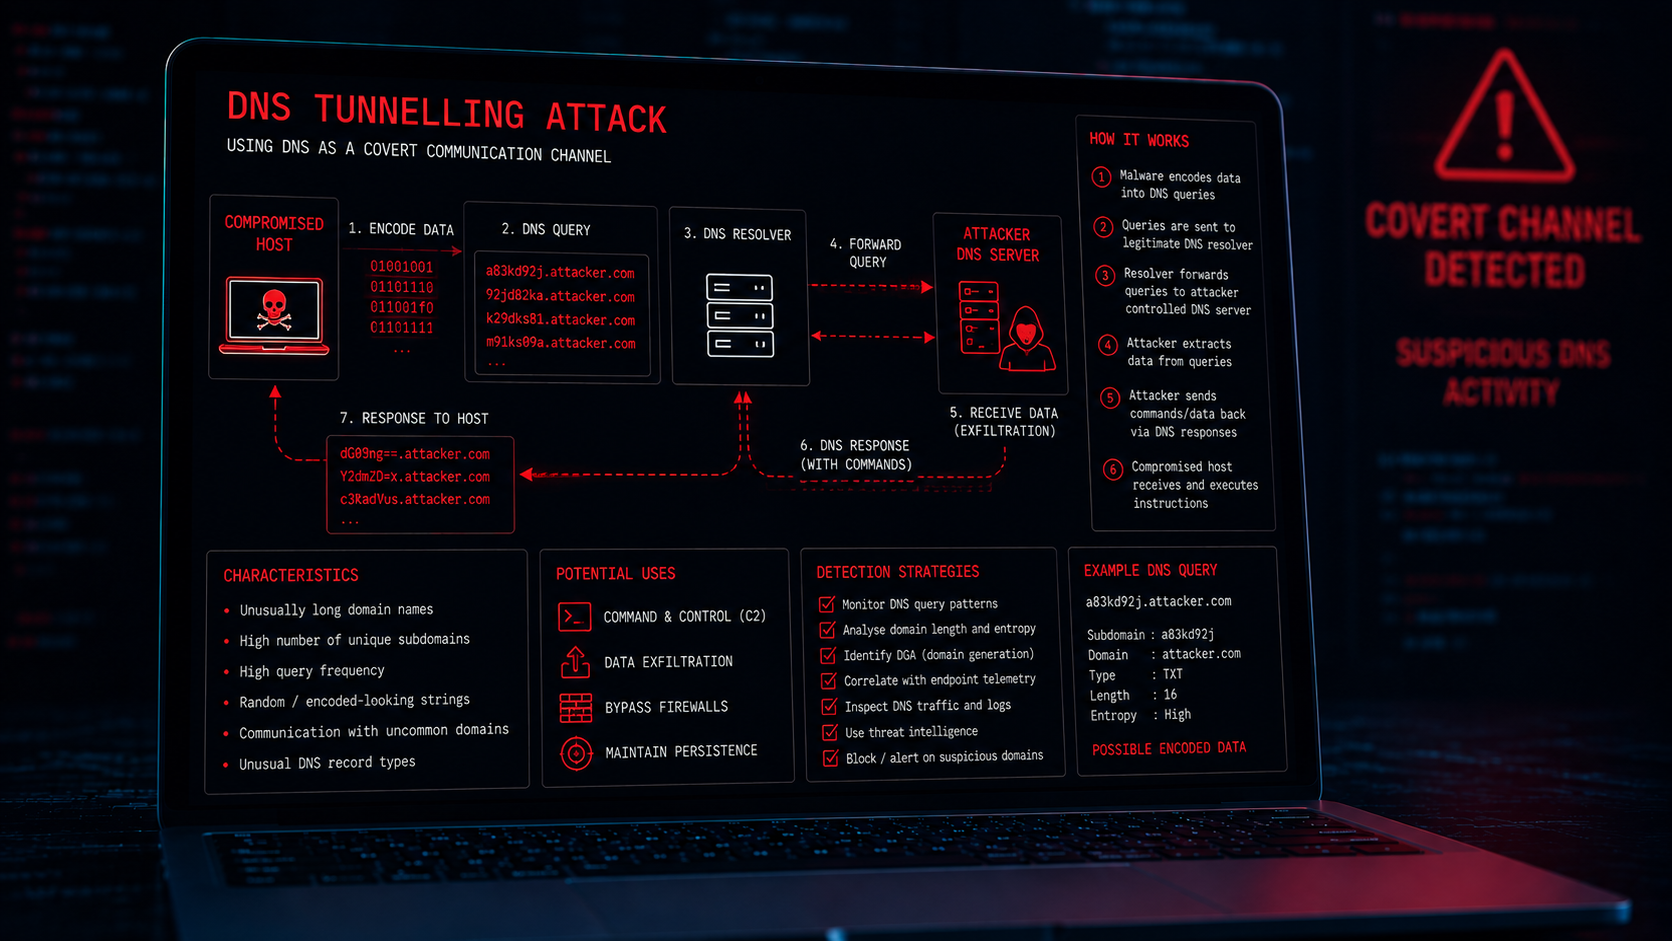 DNS tunnelling
Abusing DNS to hide communications and move data.
-
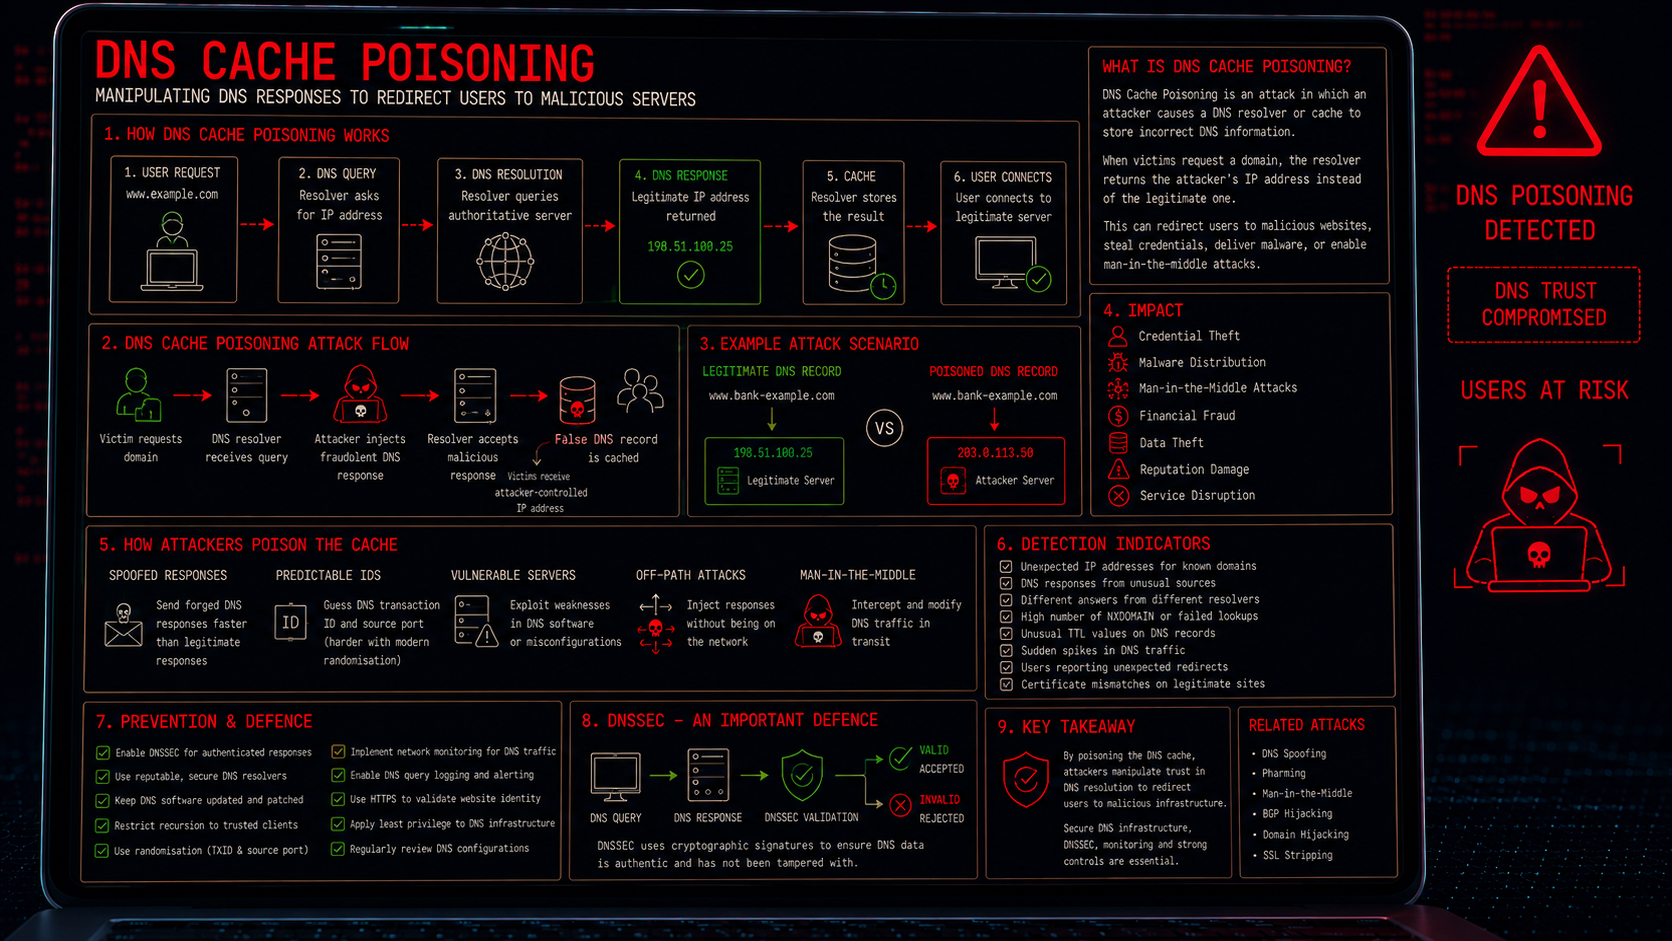 DNS poisoning & injection
Forcing DNS to store fake data.
-
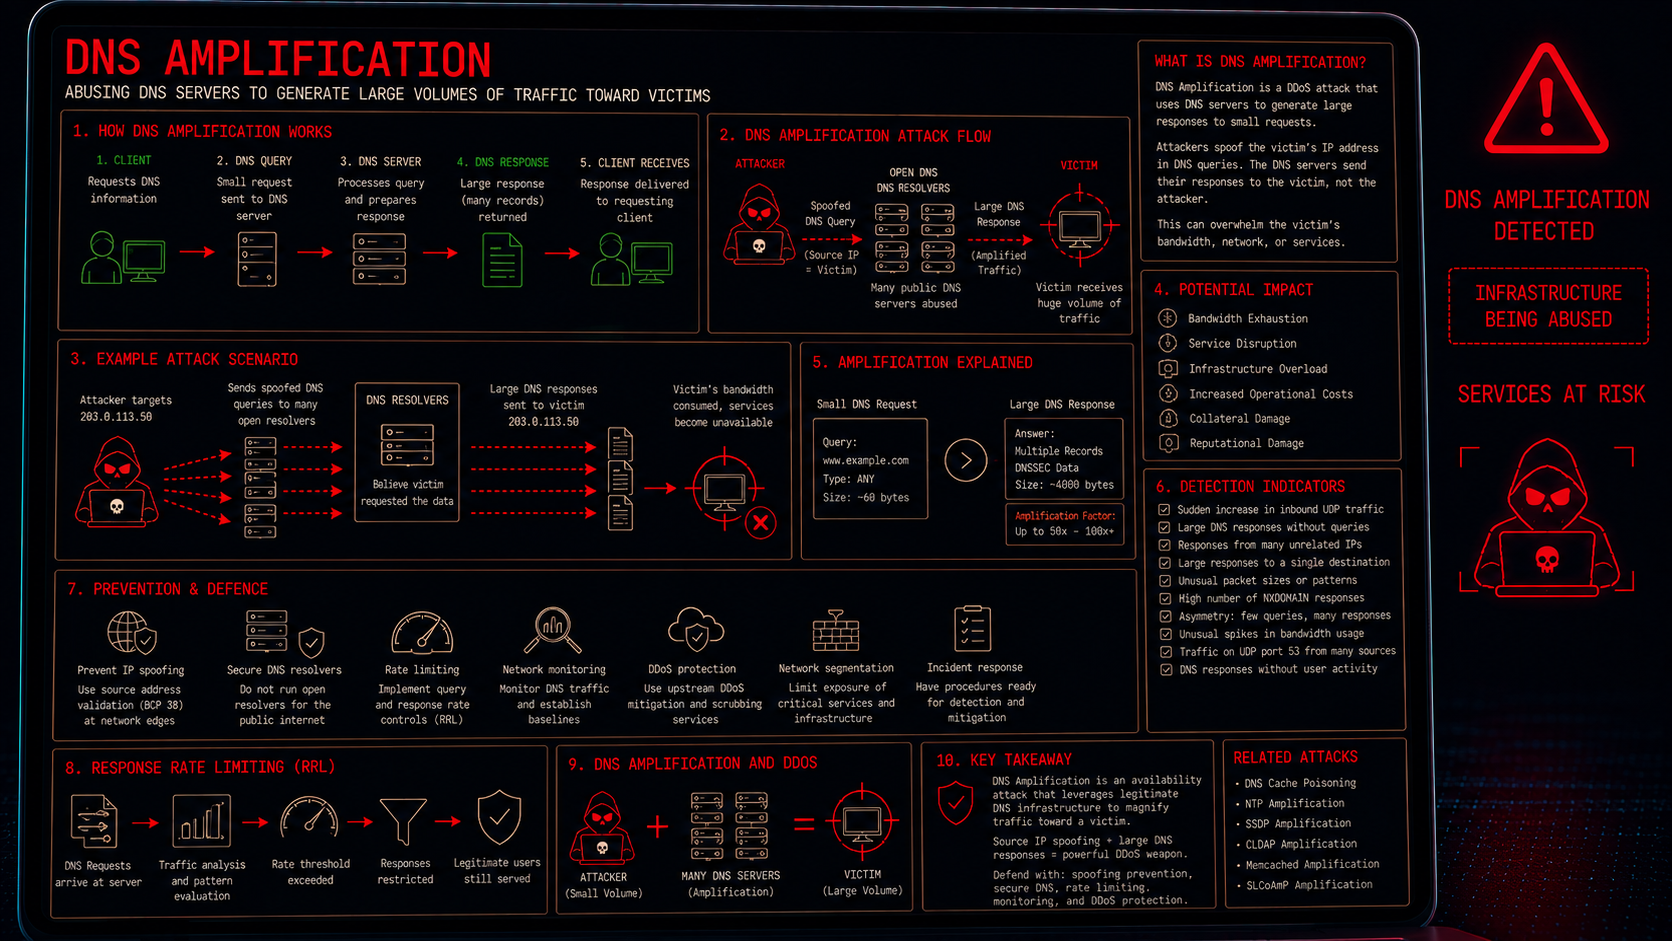 DNS amplification
Abusing DNS services as a DDoS tactic.
-
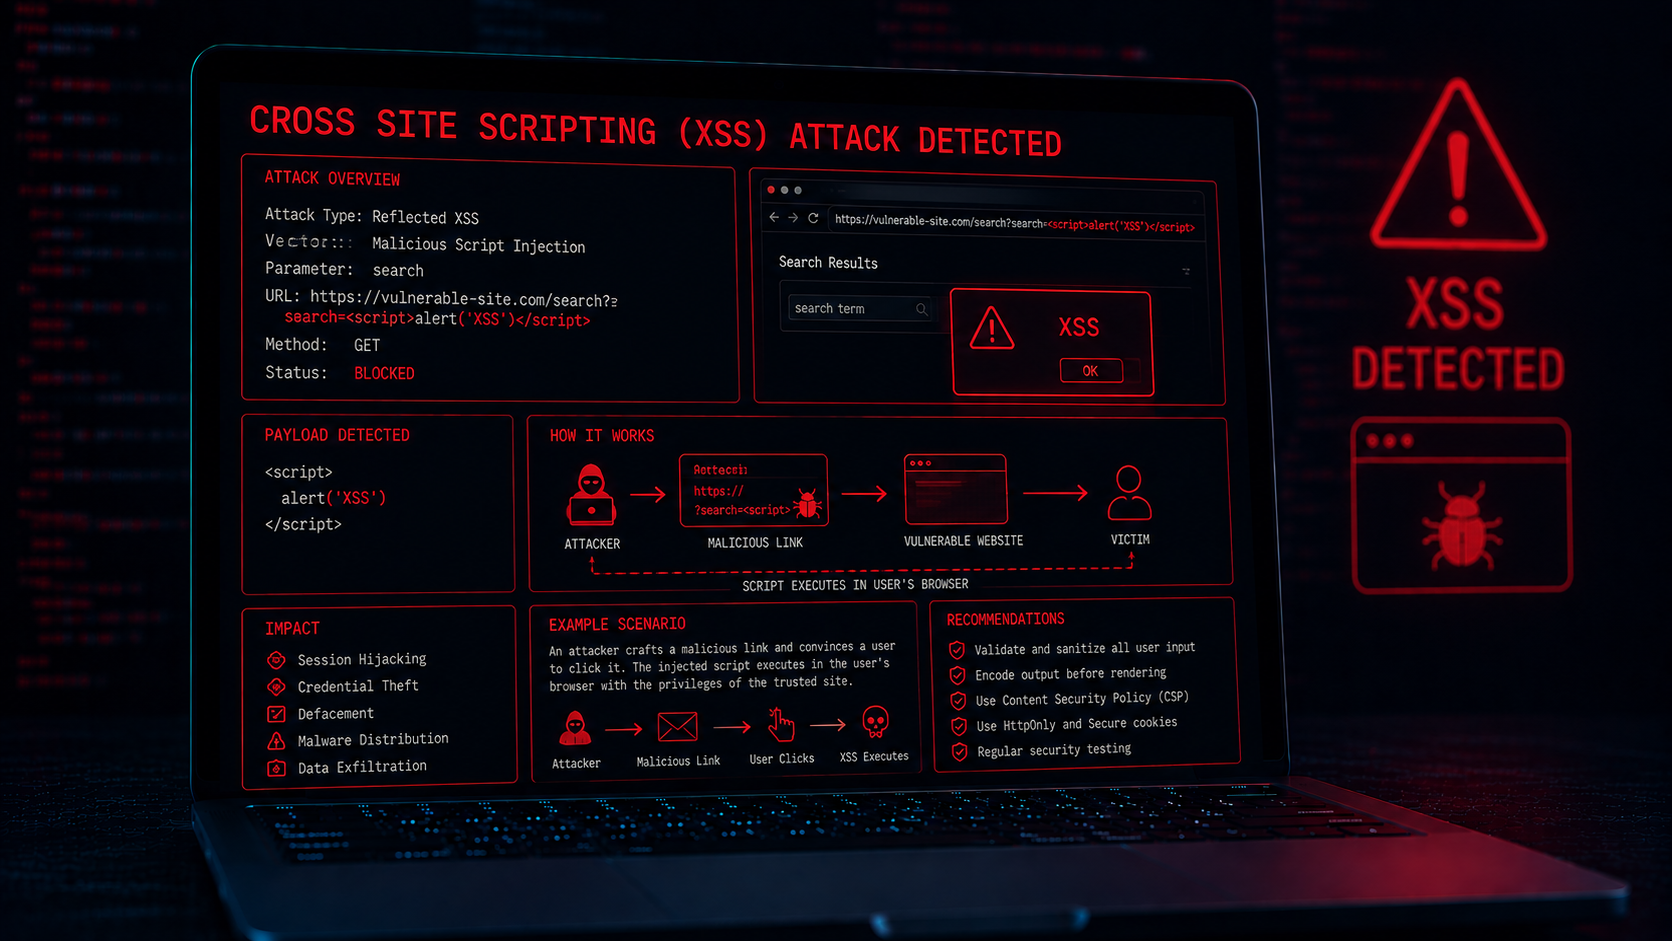 Cross Site Scripts (XSS)
Getting a browser to run script it should never have trusted.
-
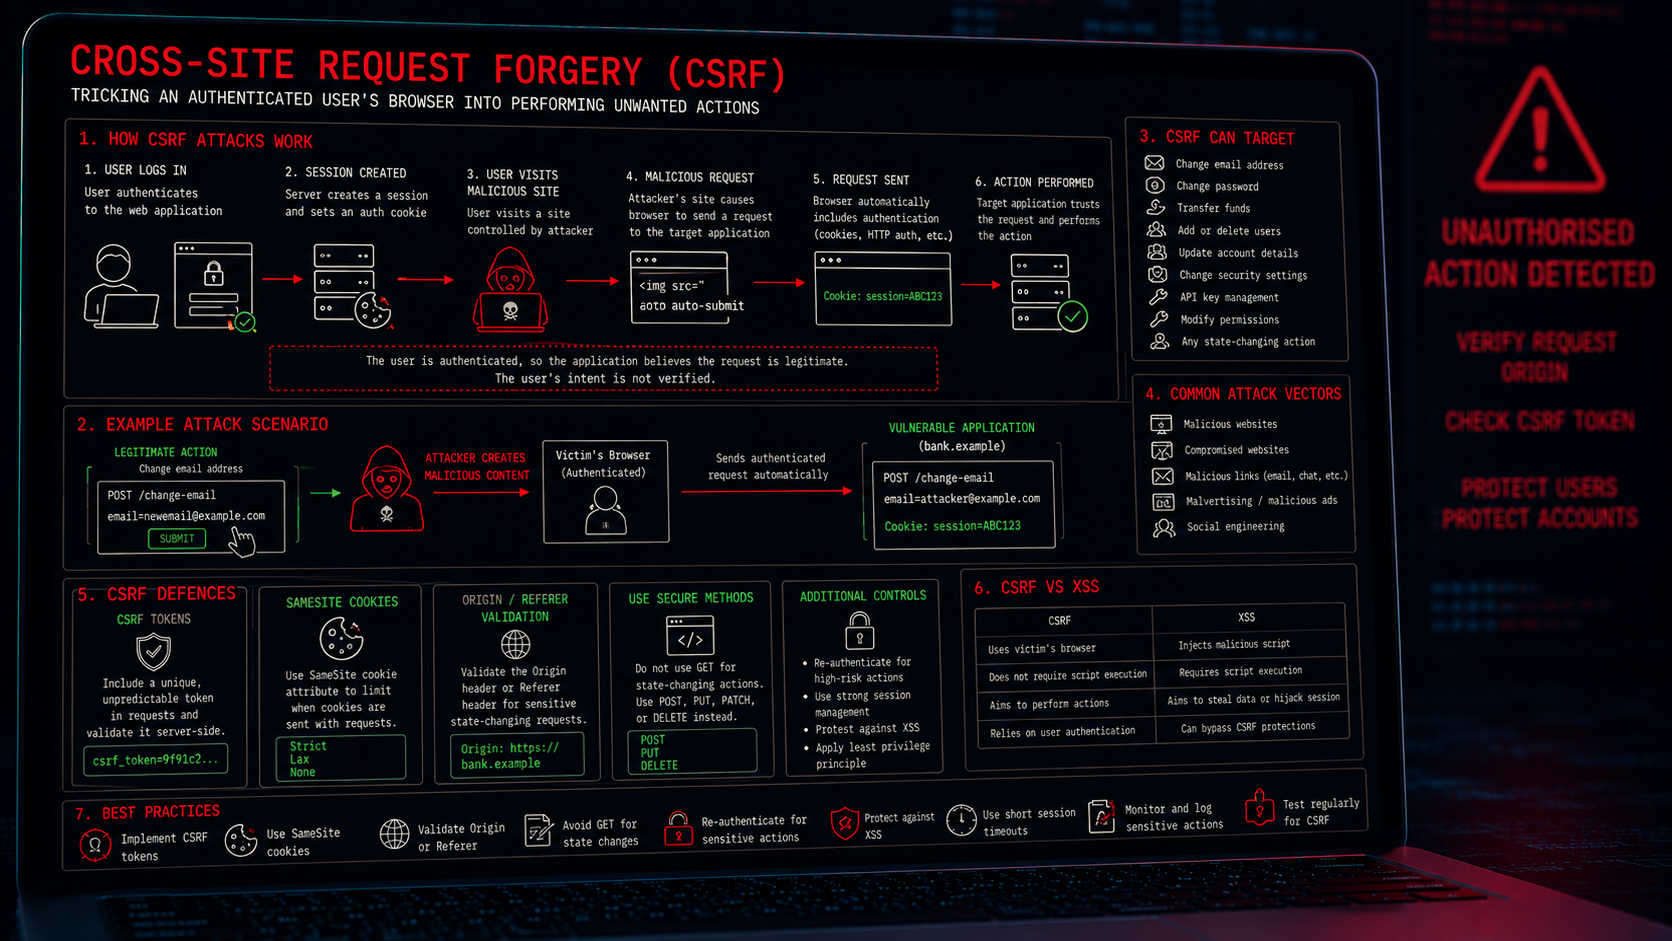 Cross-Site Request Forgery (CSRF)
Tricking authenticated users into performing unwanted actions.
-
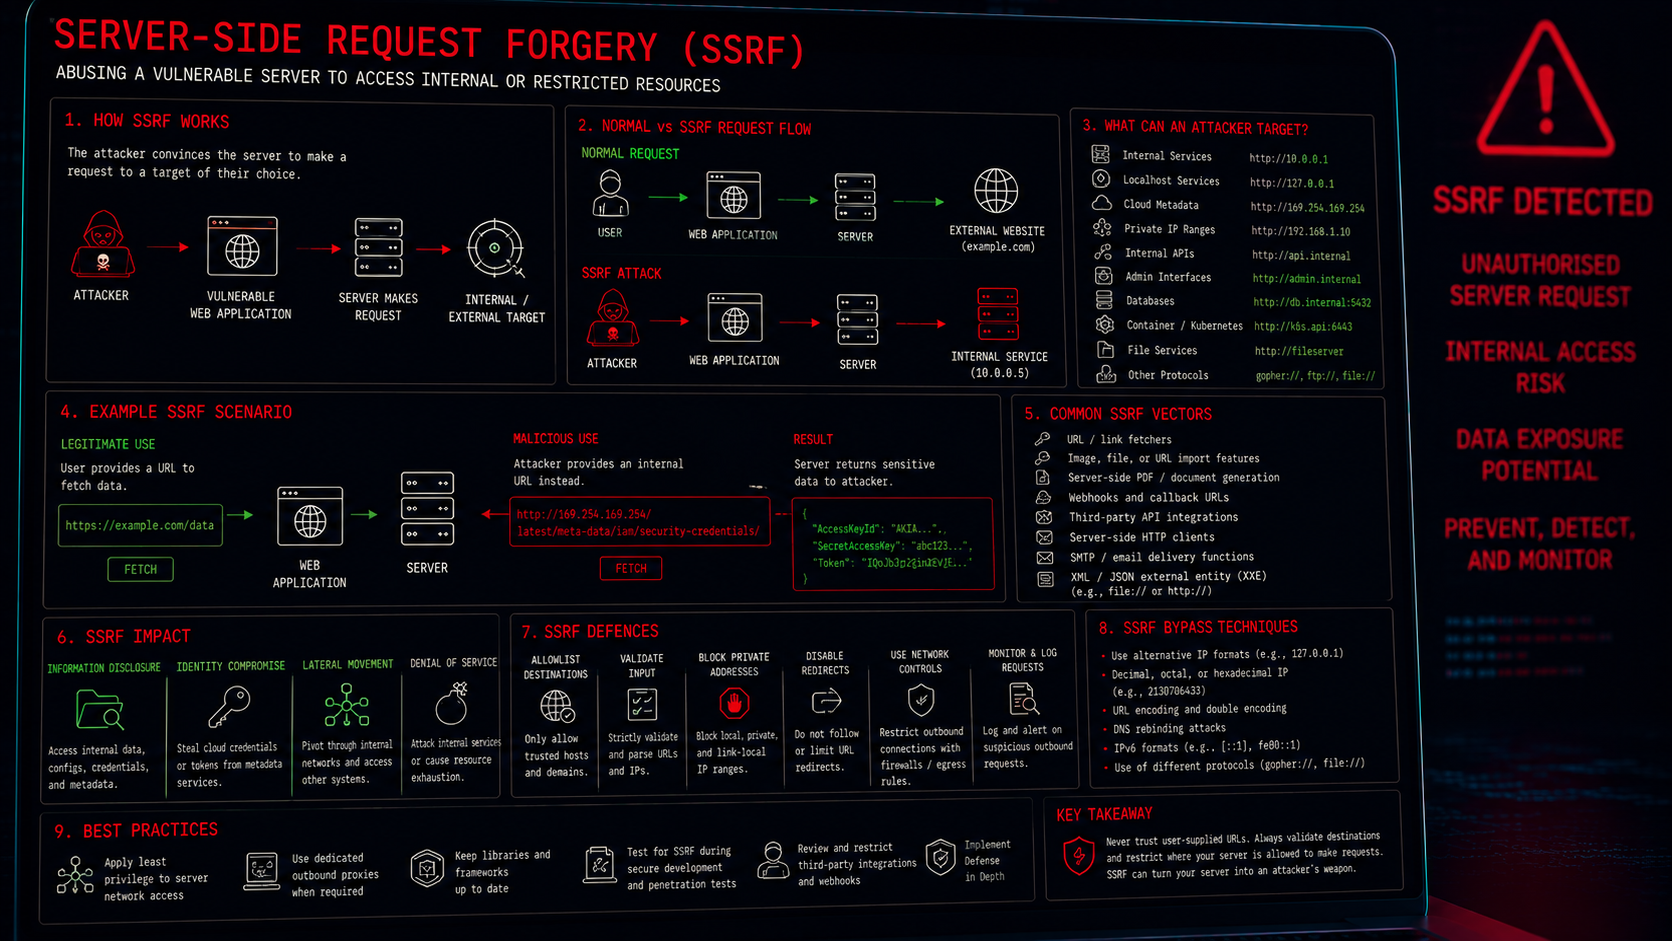 Server-Side Request Forgery (SSRF)
Abusing a vulnerable server to make requests to systems that should not be directly accessible.
-
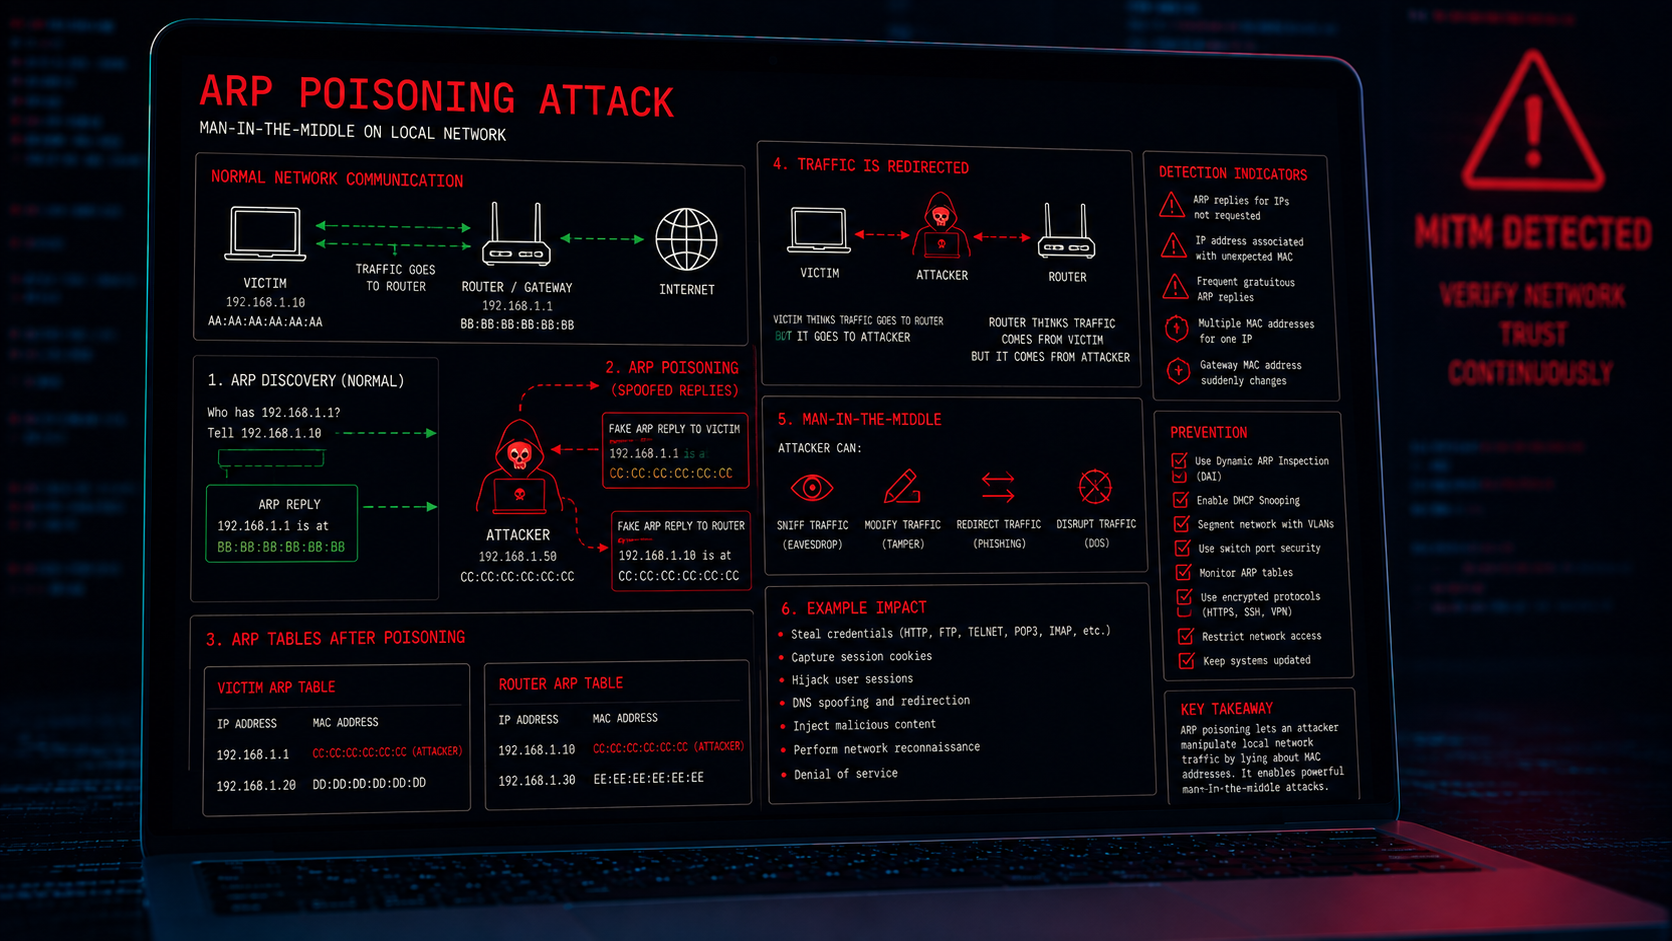 ARP poisoning
Manipulating network traffic to intercept, redirect, or disrupt communications.
-
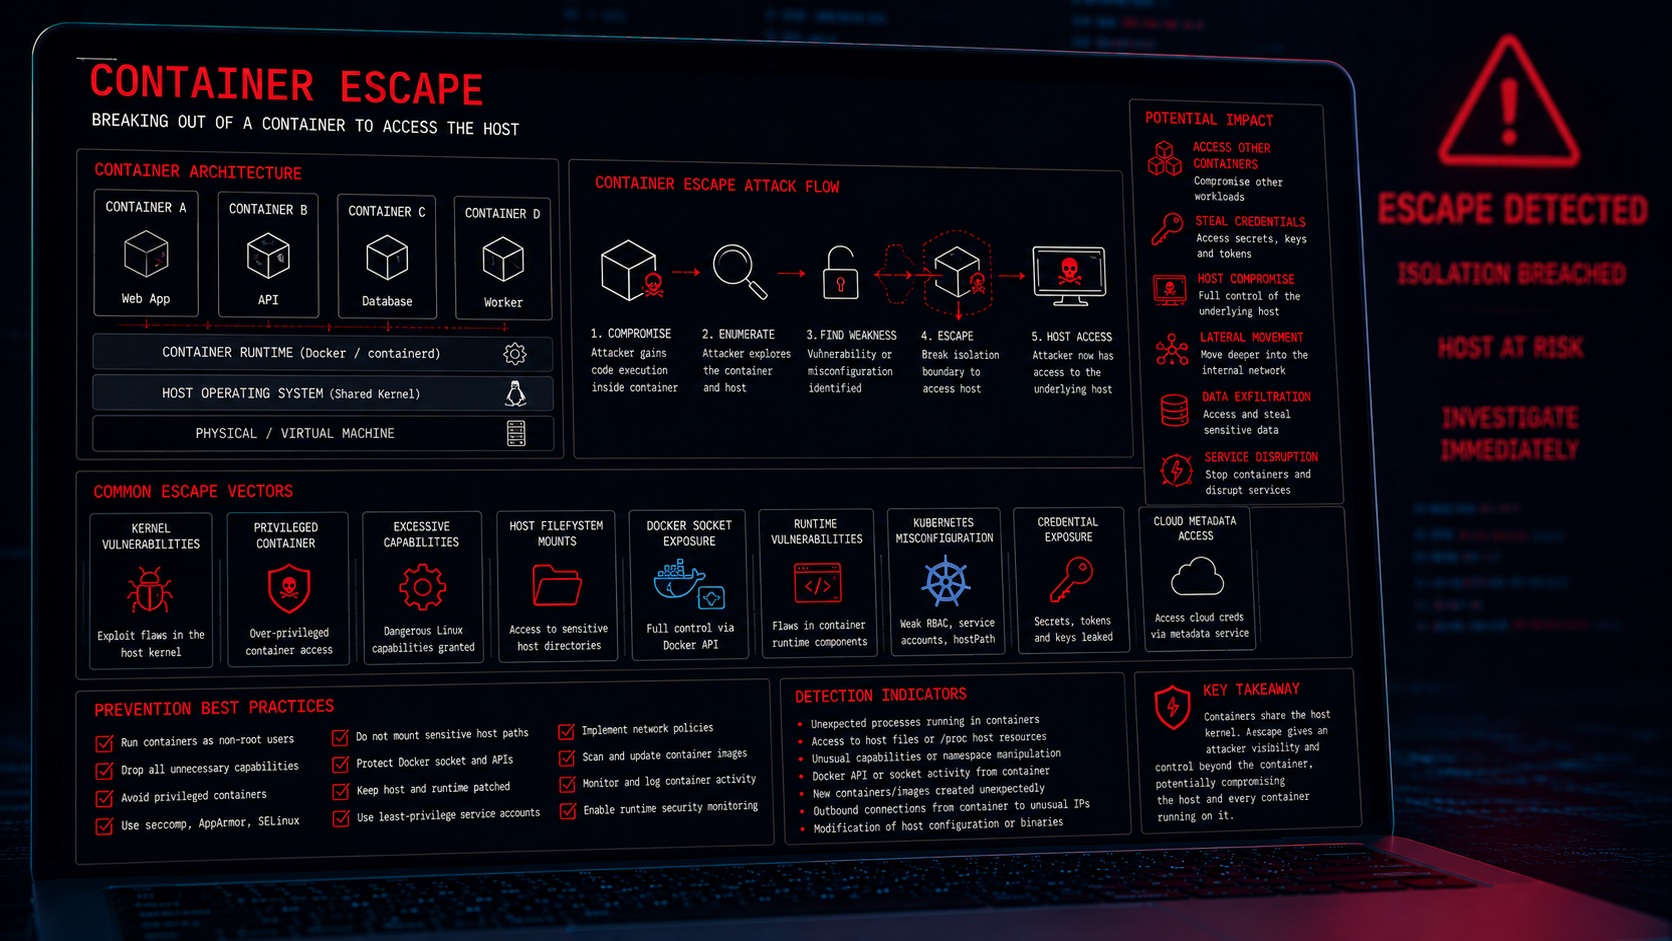 Container escape
Attacking virtual systems to access the underlying host or other applications.
-
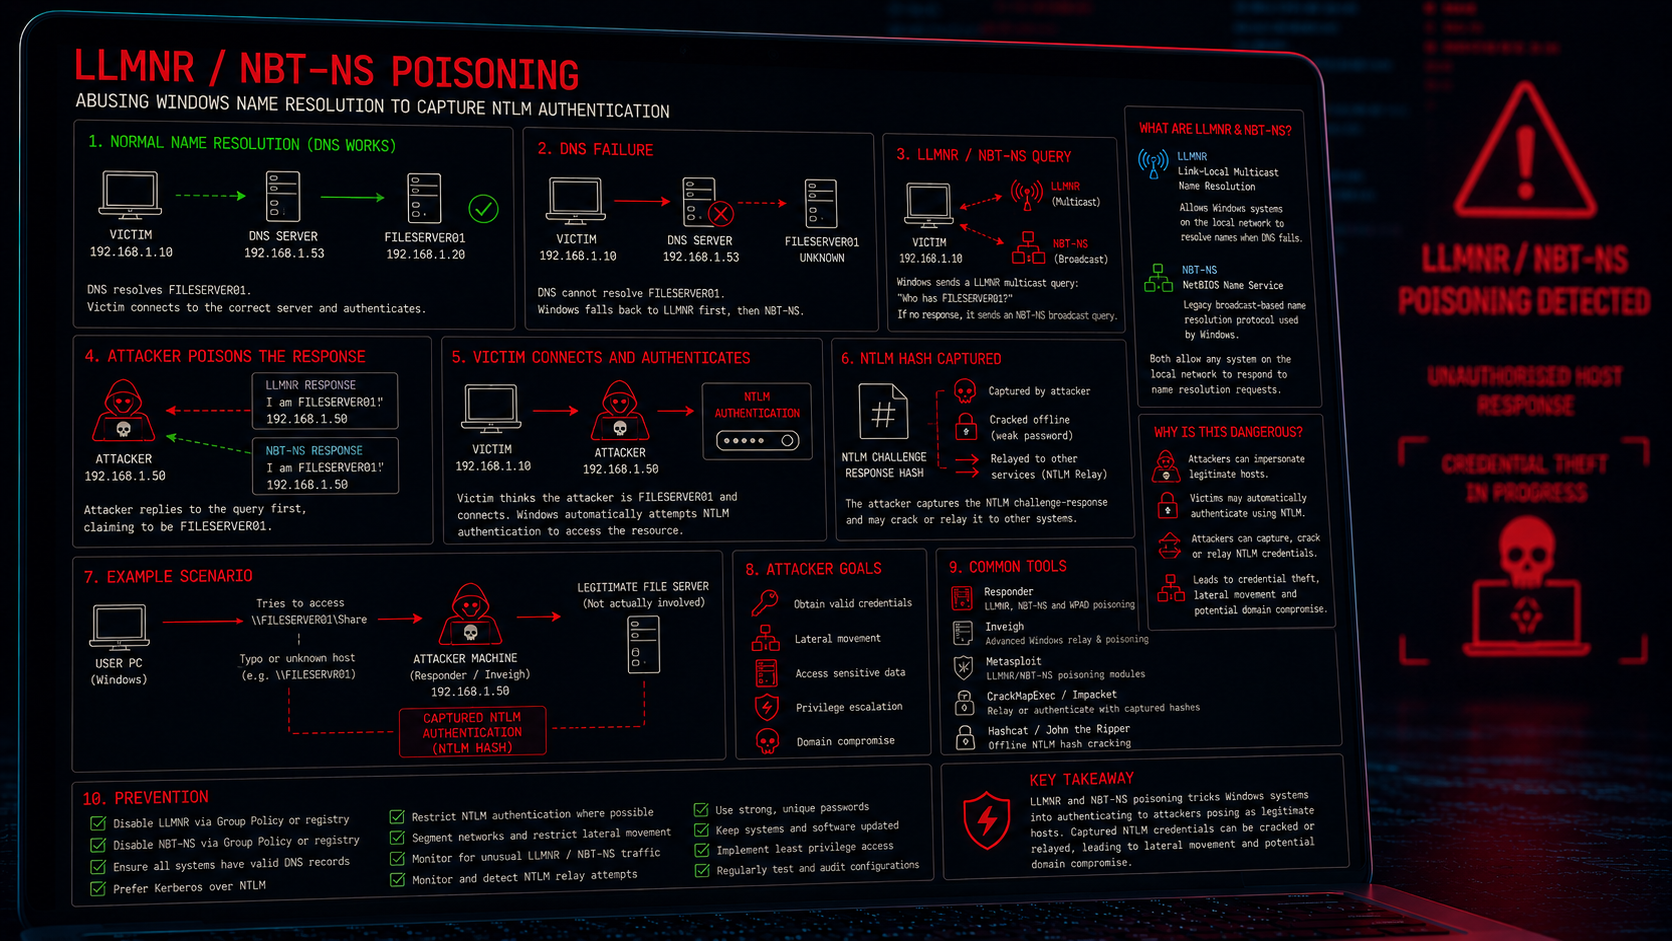 LLMNR / NBT-NS Poisoning
Abusing legacy Windows name-resolution protocols.
-
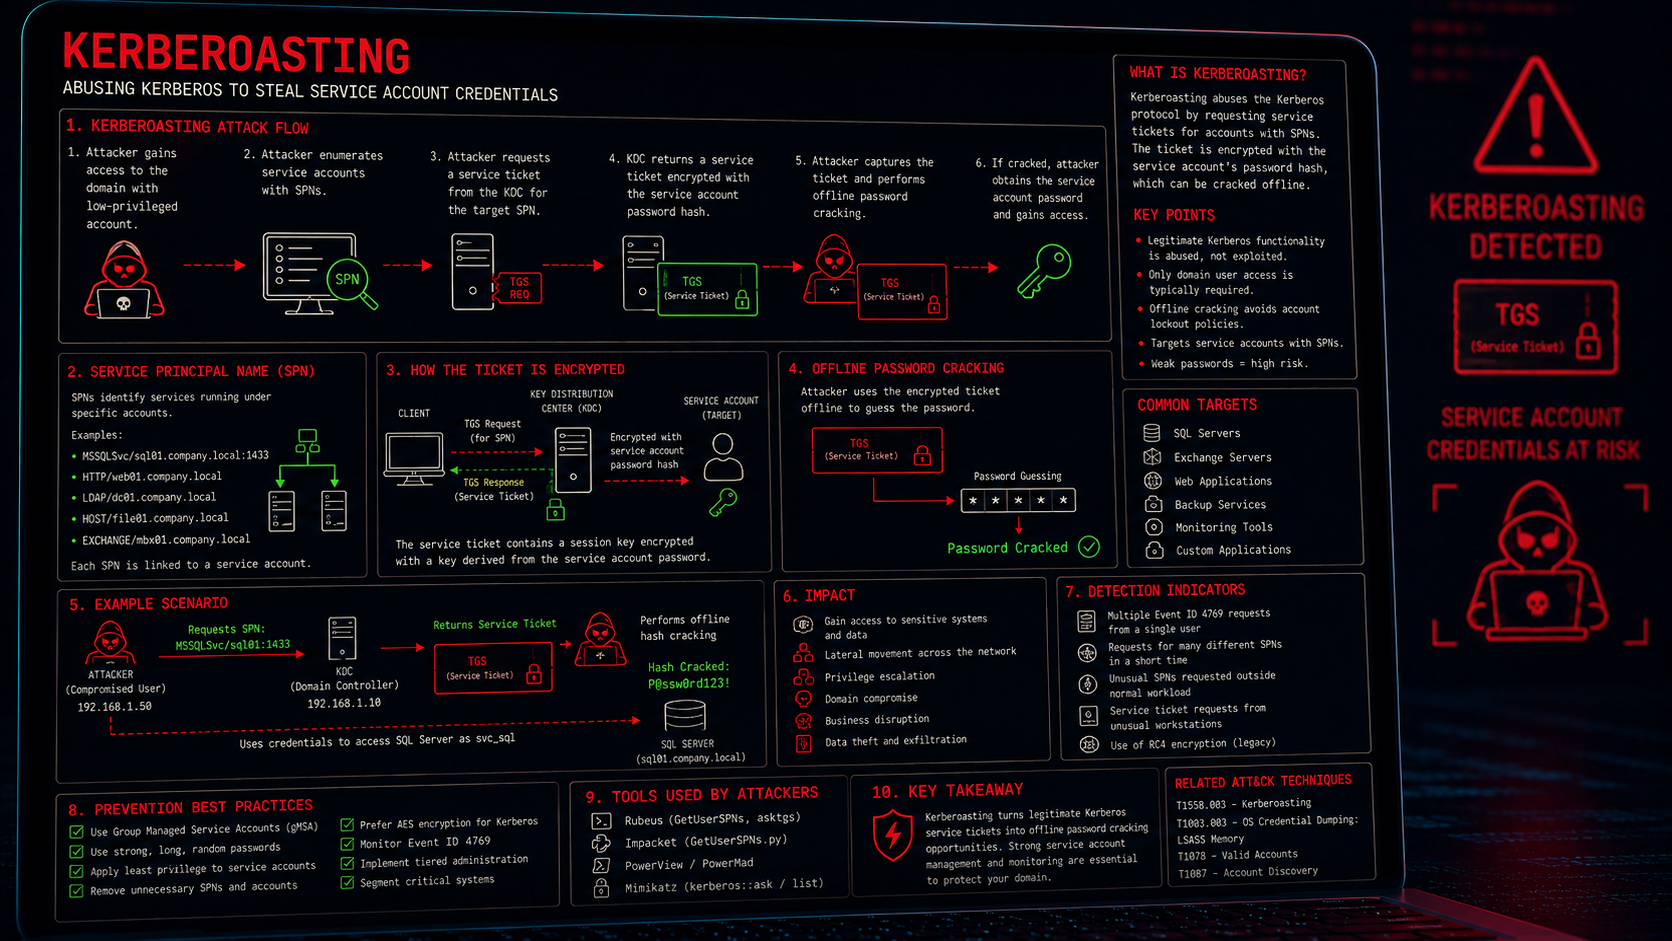 Kerberoasting
Stealing service account credentials from Active Directory.
-
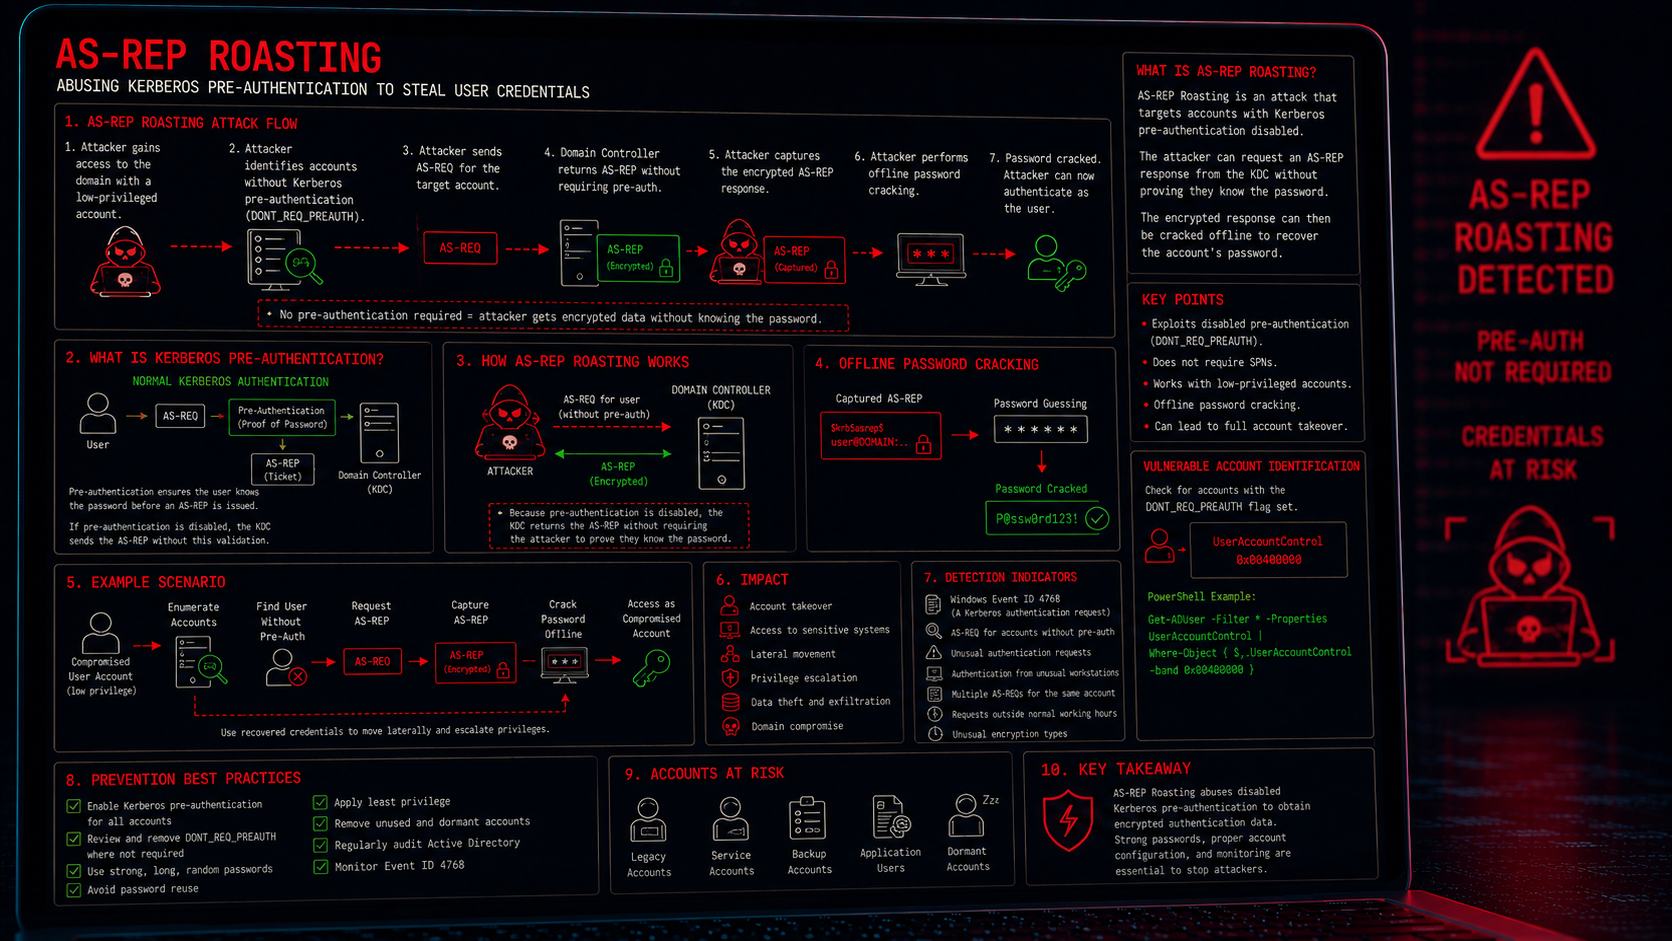 AS-REP roasting
Stealing Active Directory credentials by abusing Kerberos pre-authentication.
-
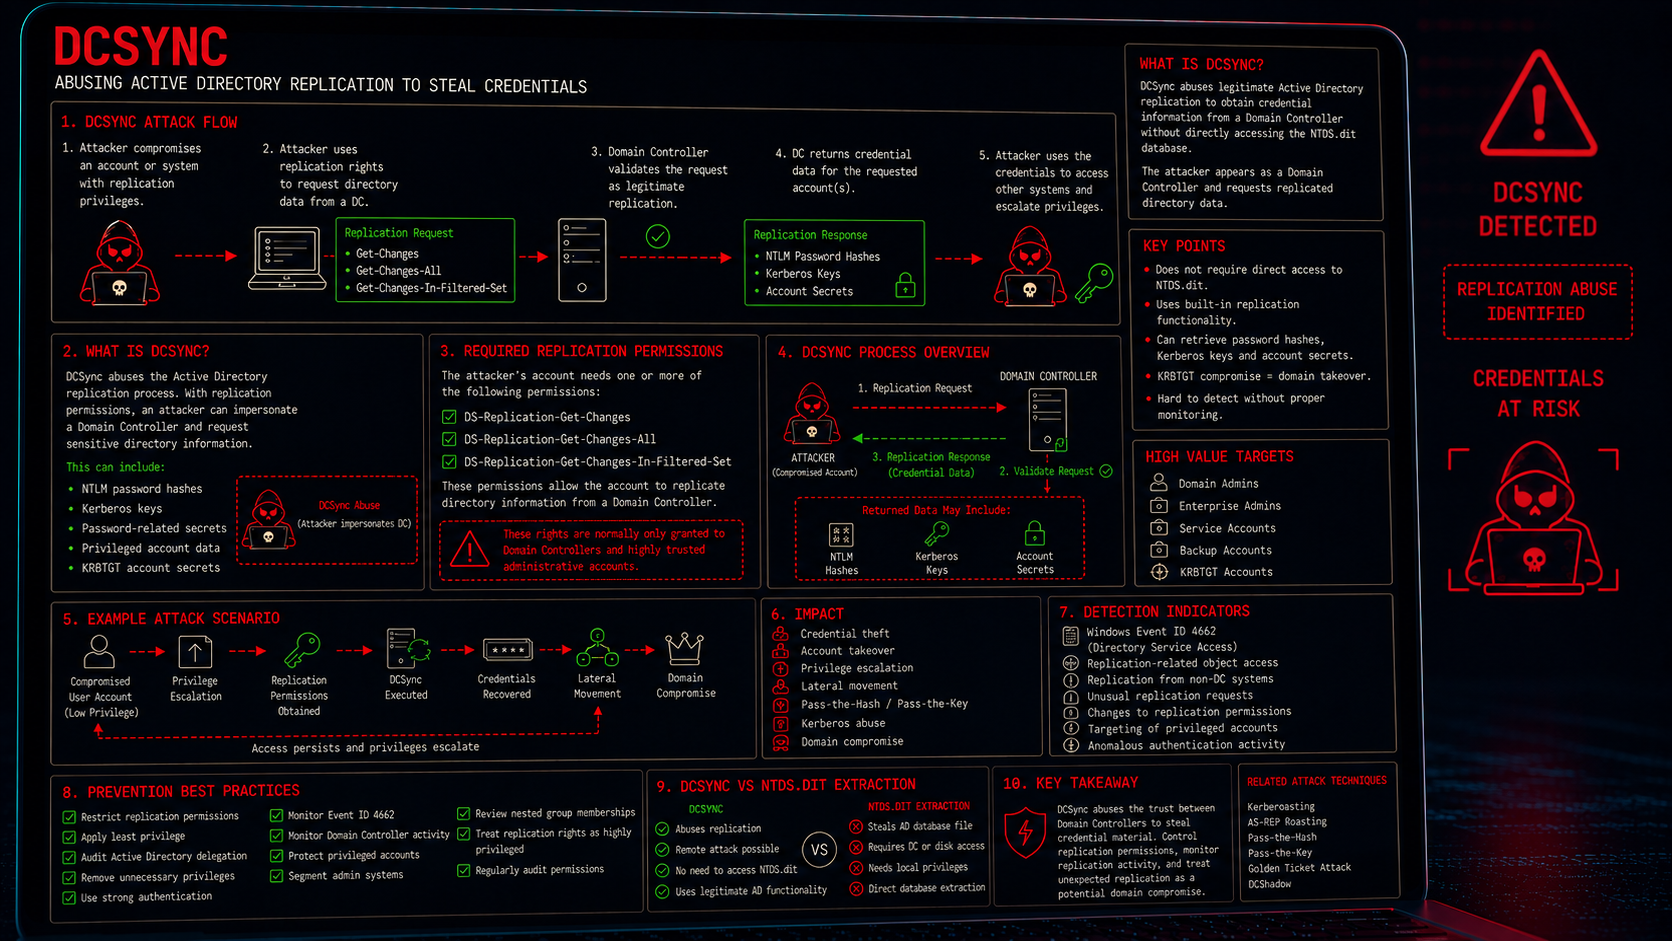 DCSync
Using directory replication to steal secrets.
-
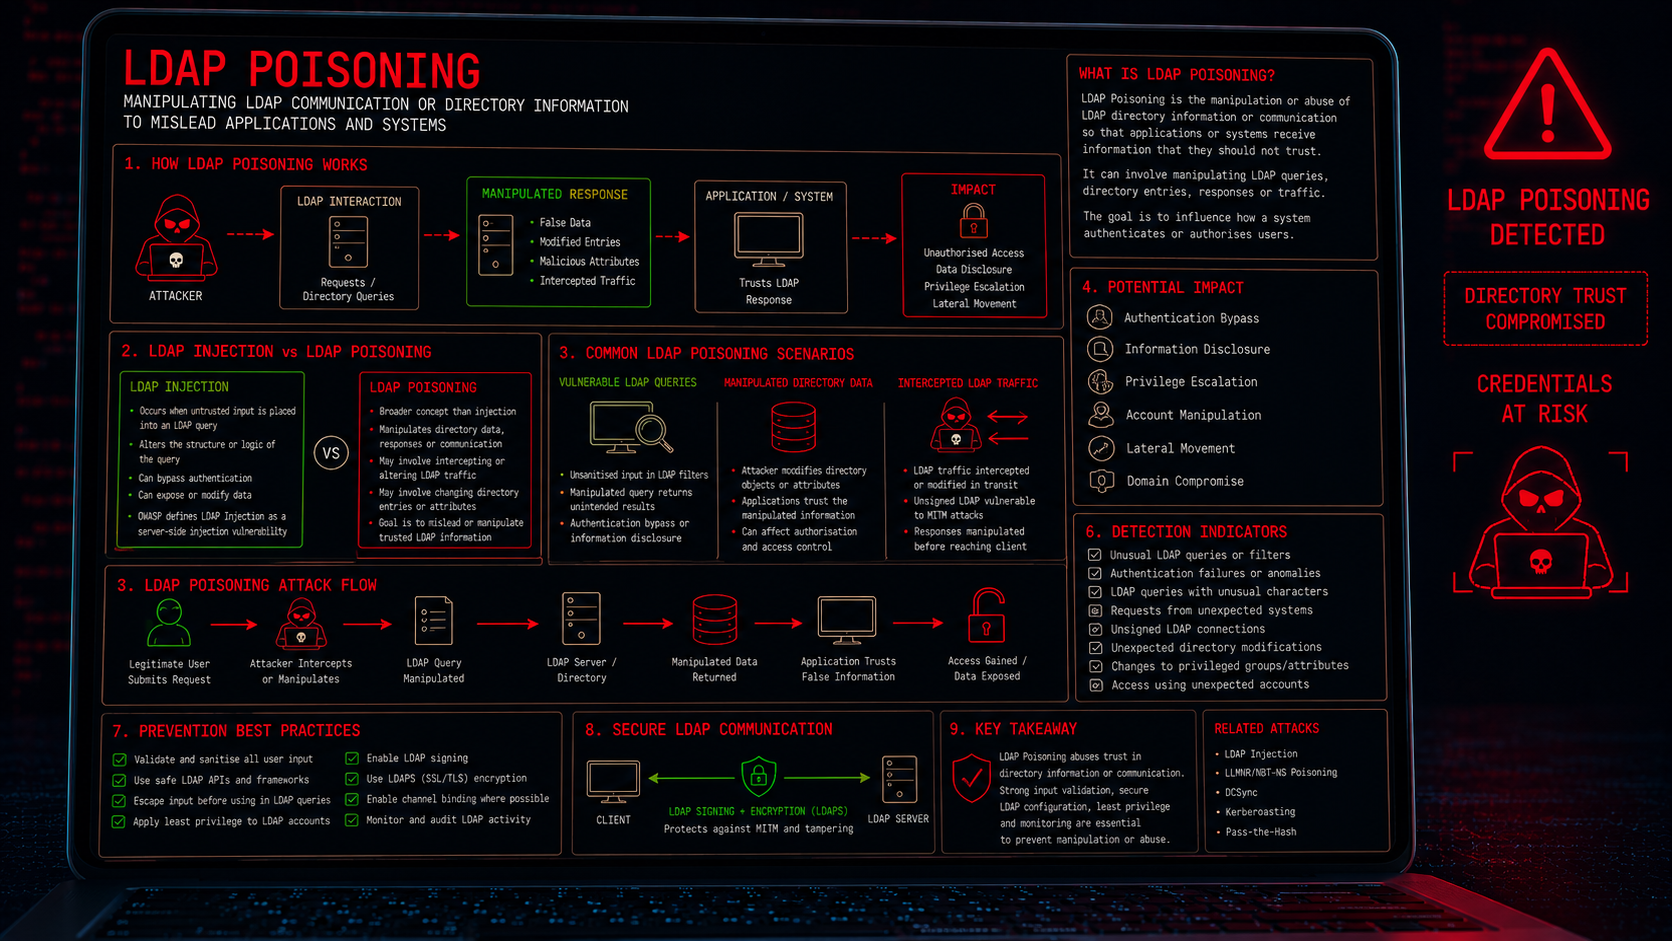 LDAP abuse
Abusing directory protocols to manipulate AD databases.
-
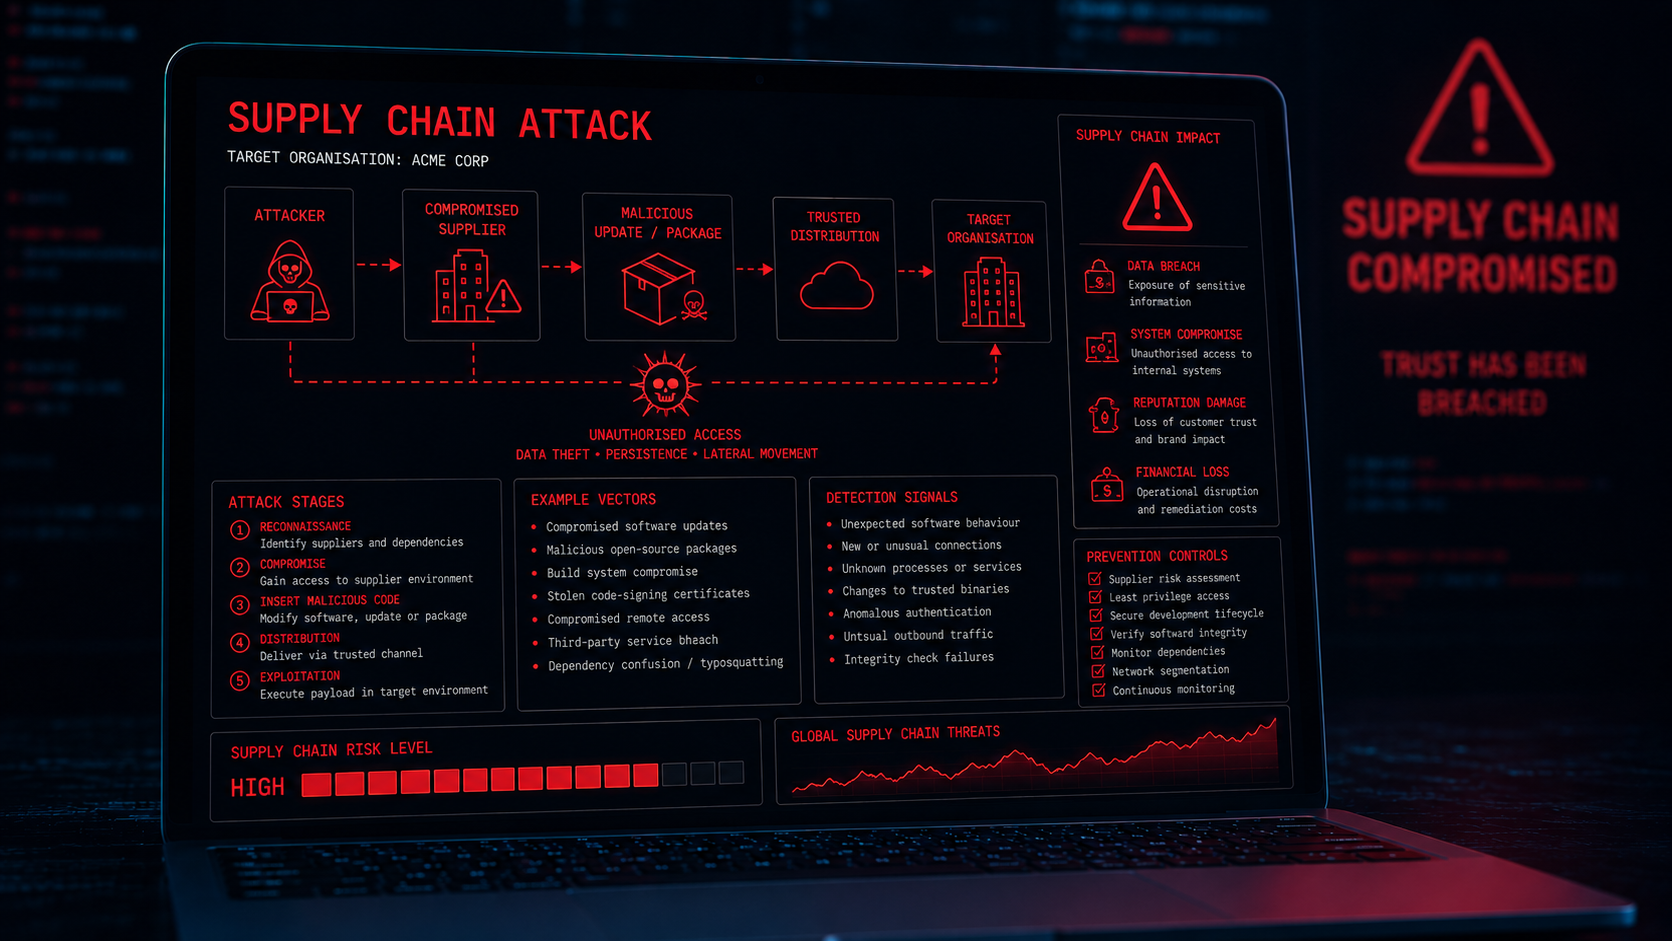 Supply Chain Attacks
Compromising trusted suppliers, software, and services
-
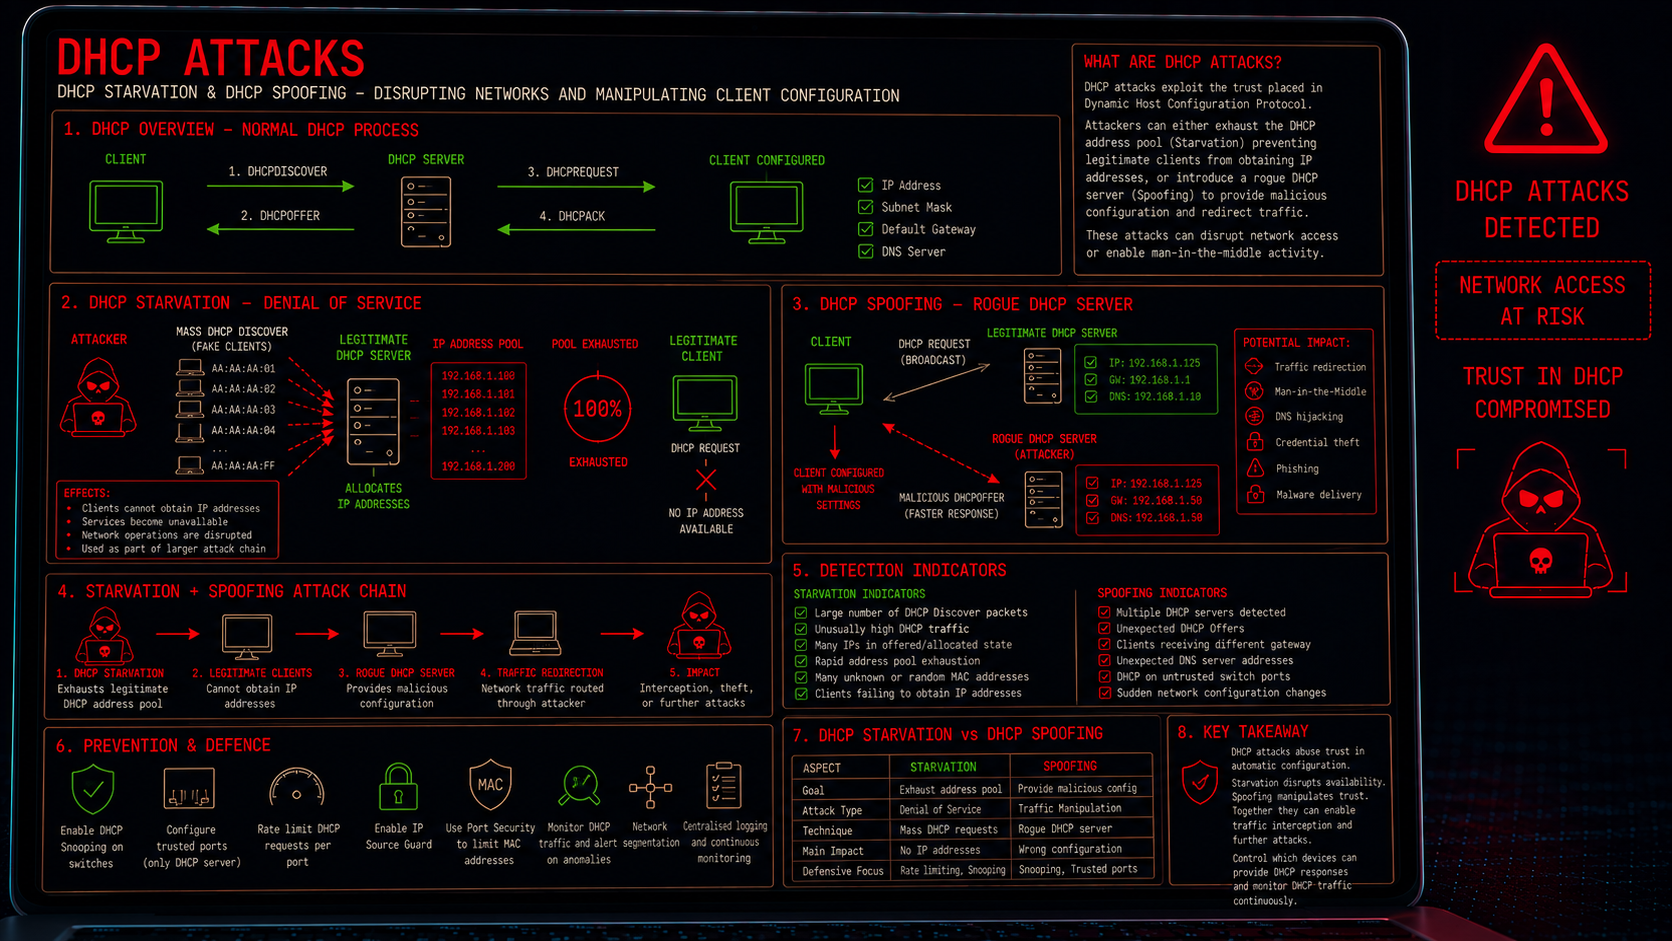 DHCP Attacks
Disrupting network configuration and redirecting traffic by abusing DHCP
-
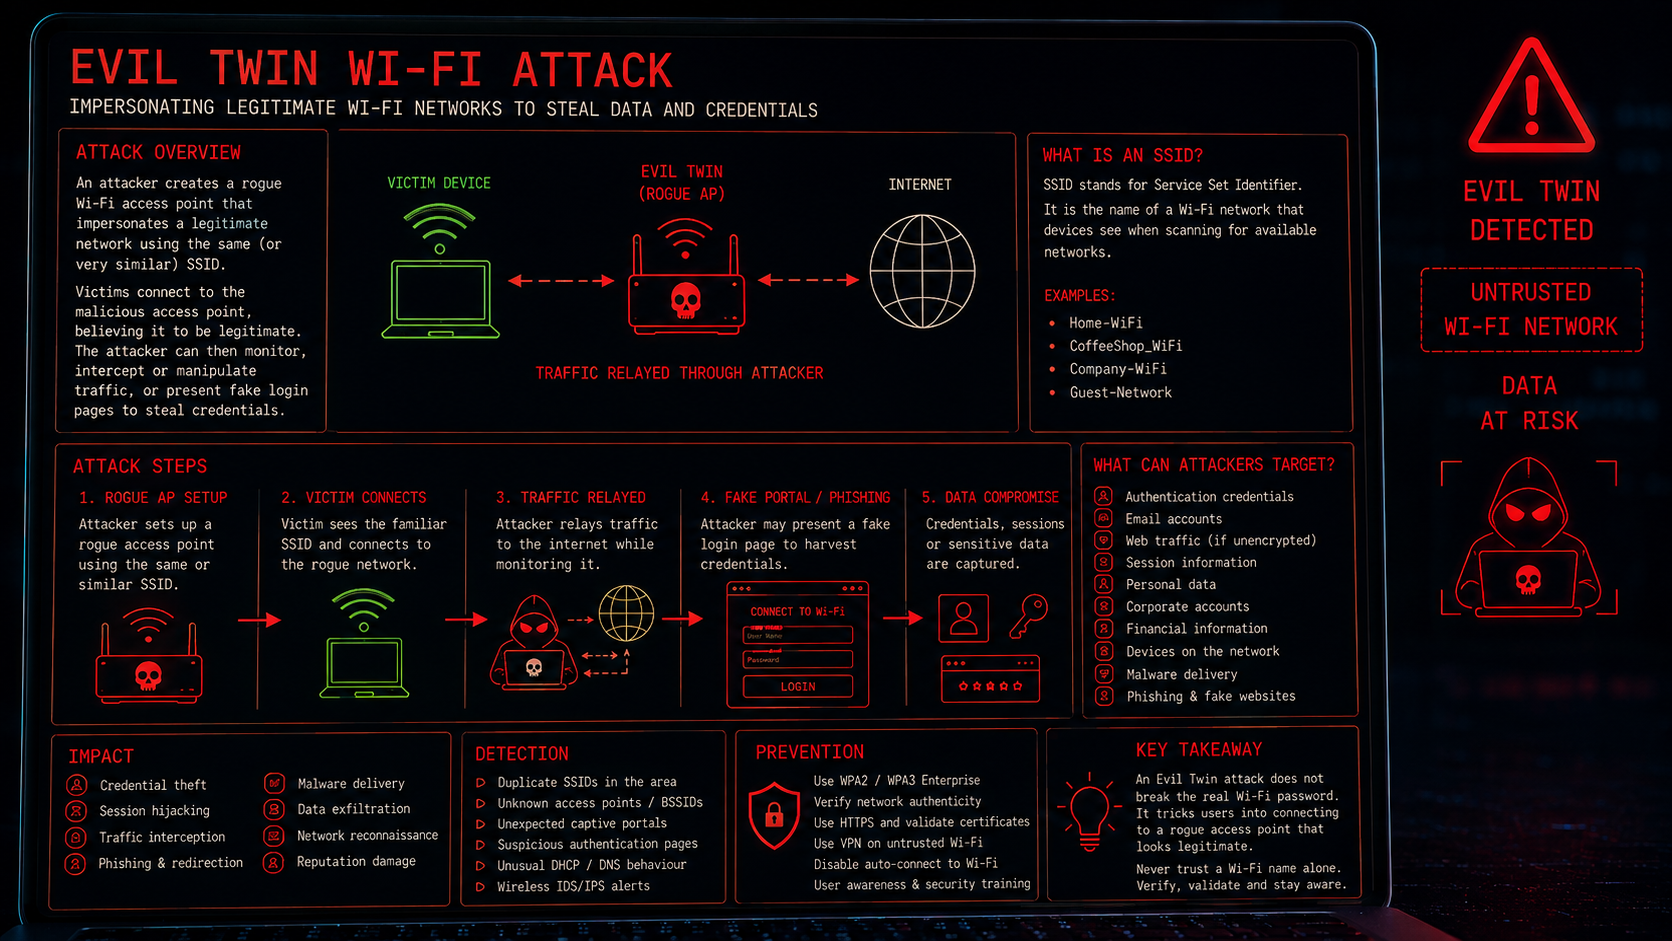 Evil Twin Wi-Fi
Tricking users to connect to a malicious network
-
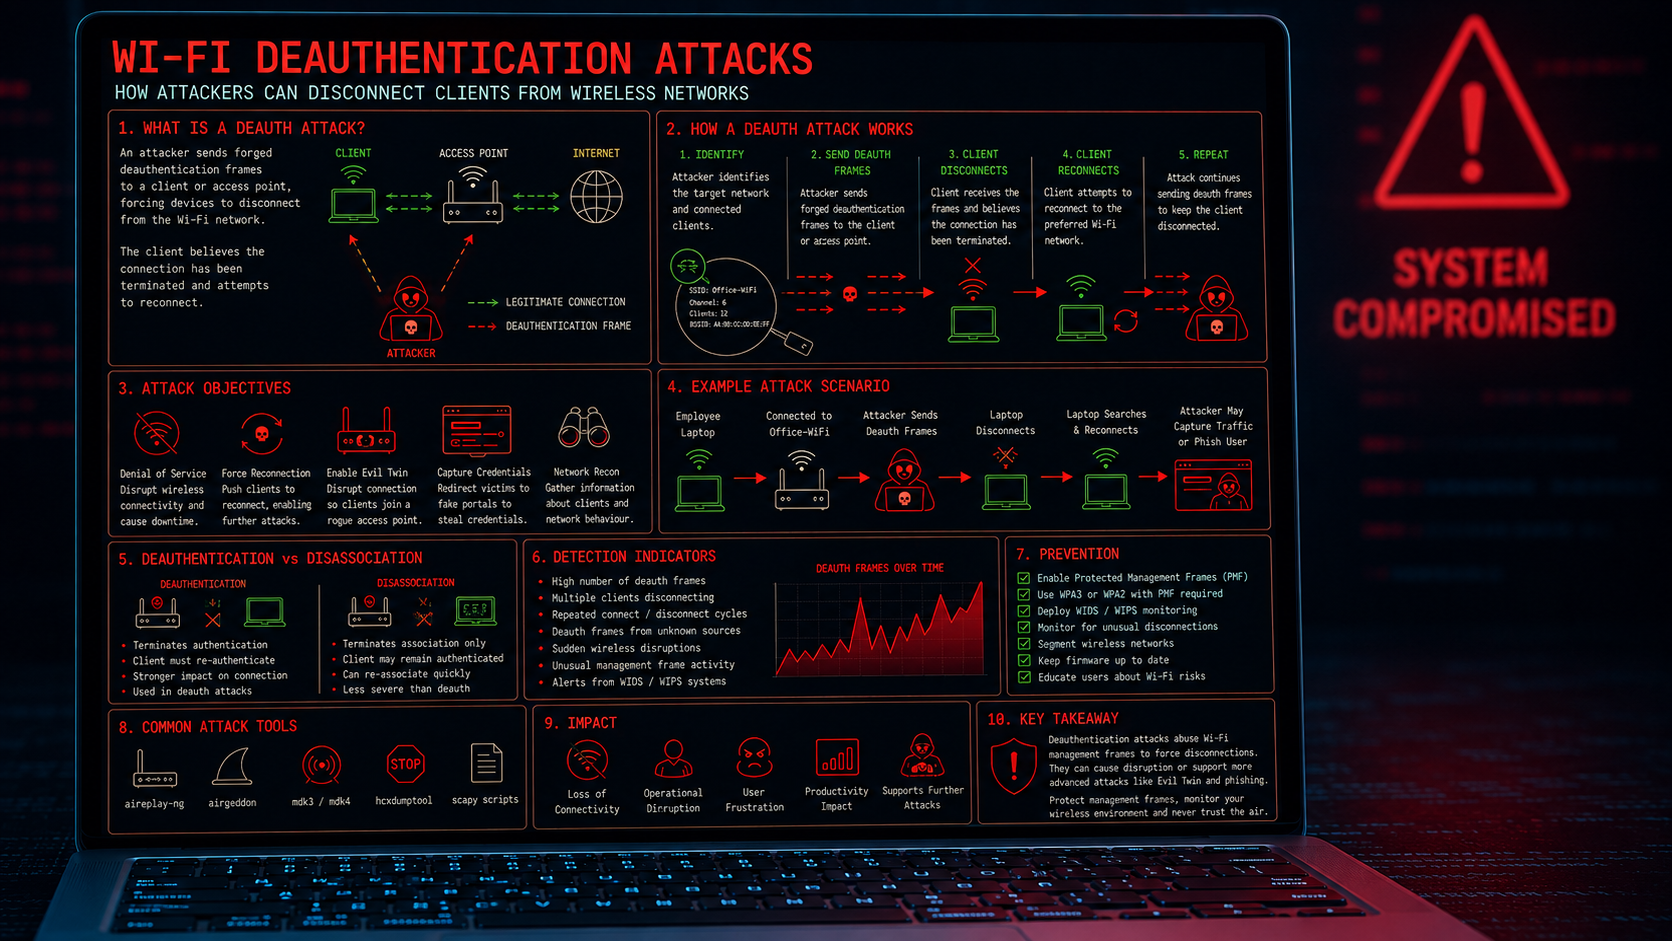 Wi-Fi Deauthentication attacks
How attackers can deliberately disconnect devices from wireless networks
-
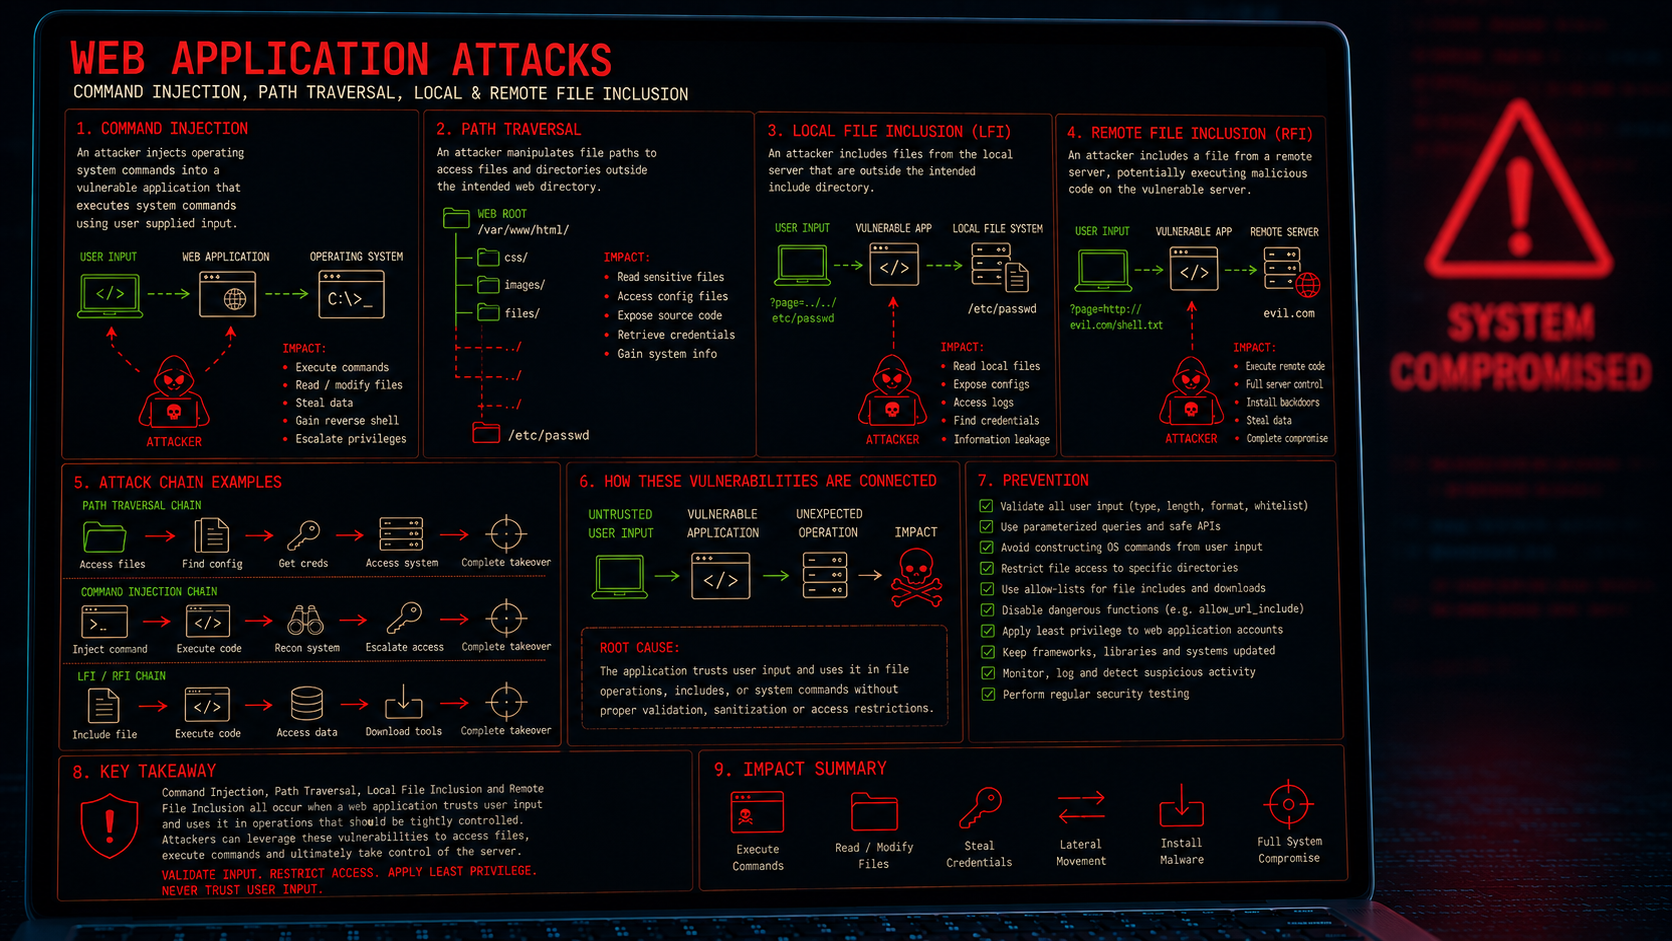 Web Application Attacks
Web app vulnerabilities can lead to data exposure, command execution, malware, and more
-
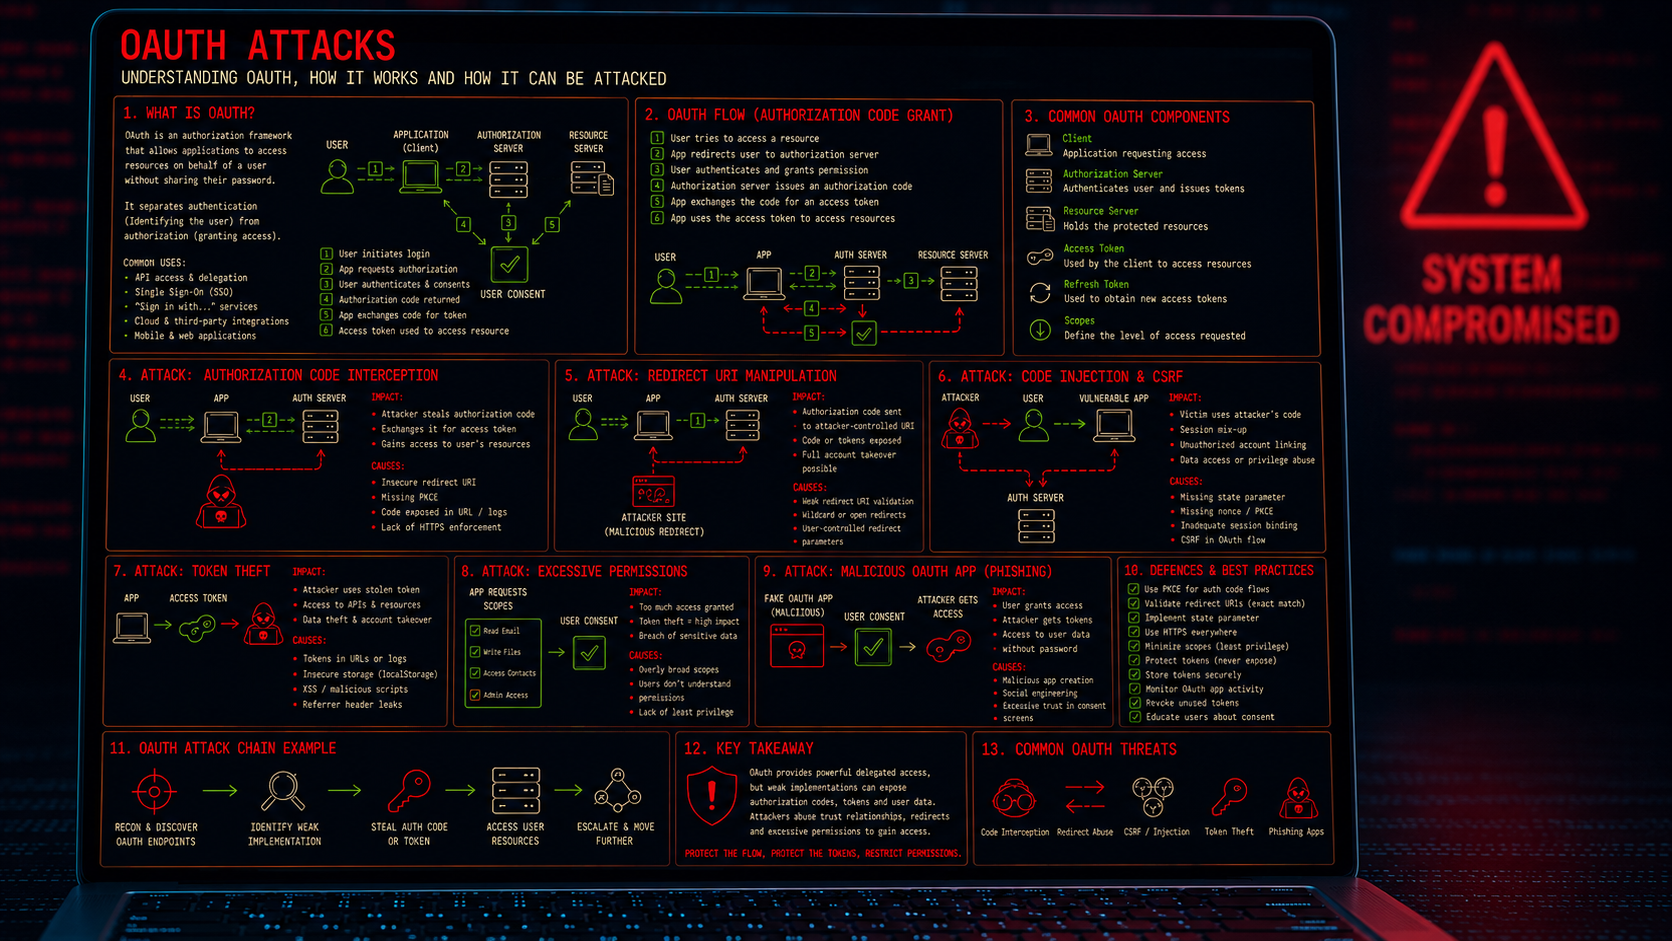 OAuth Attacks
Using a common authentication mechanism to compromise users
-
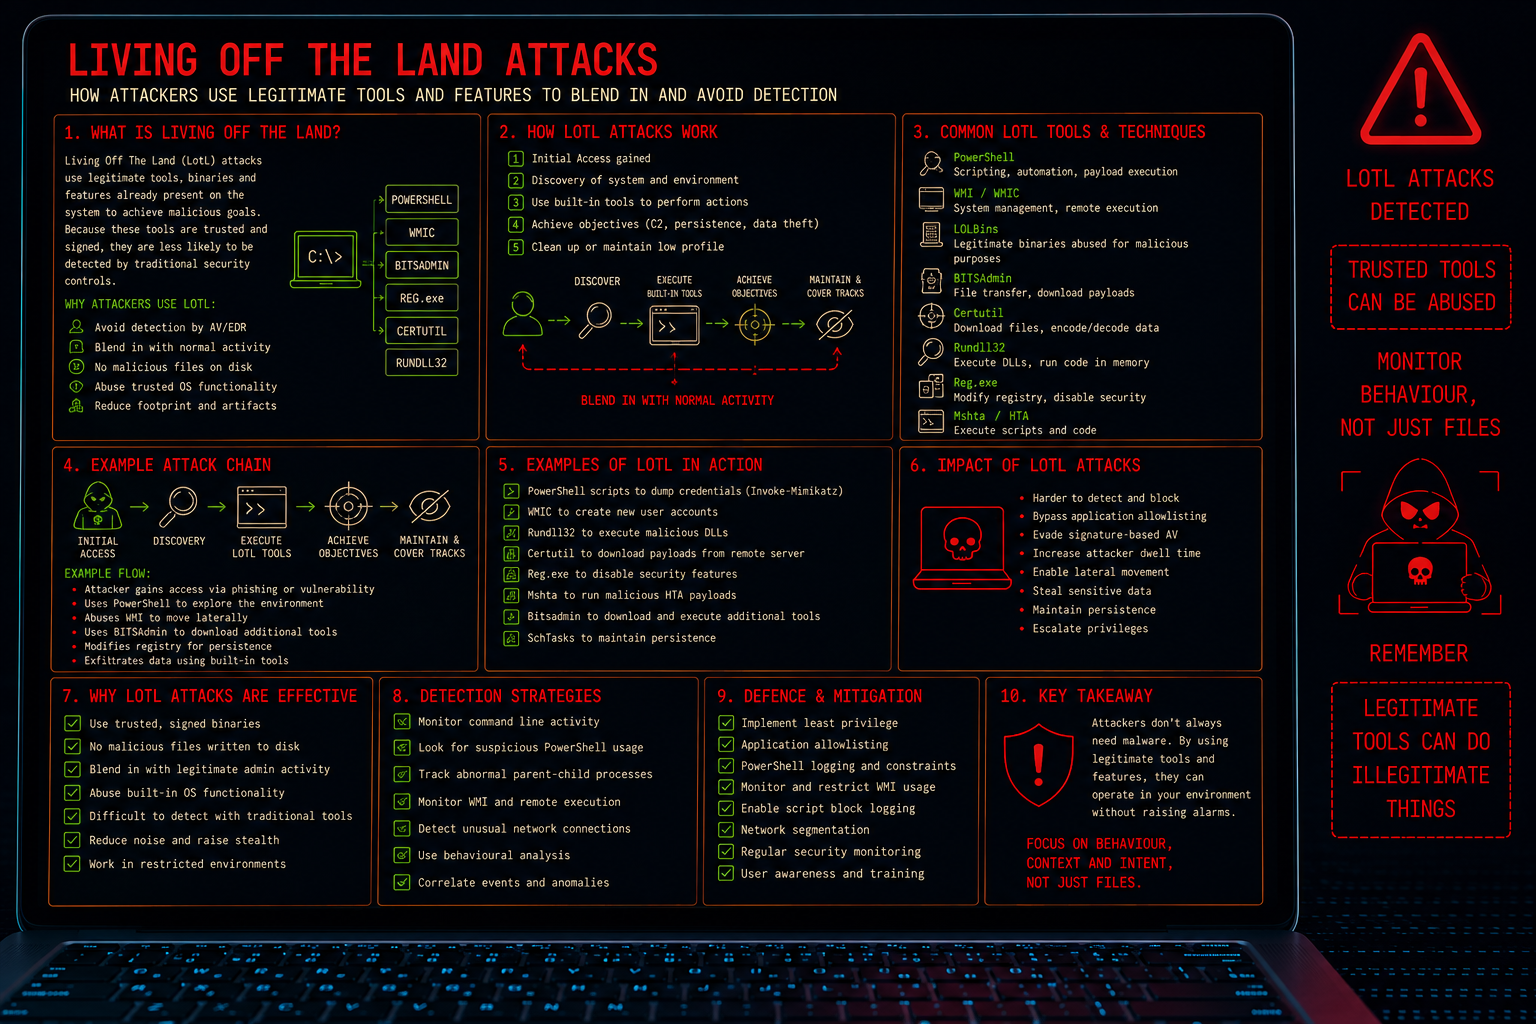 Living Off the Land (LotL)
Using legitimate tools to further an attack capability
-
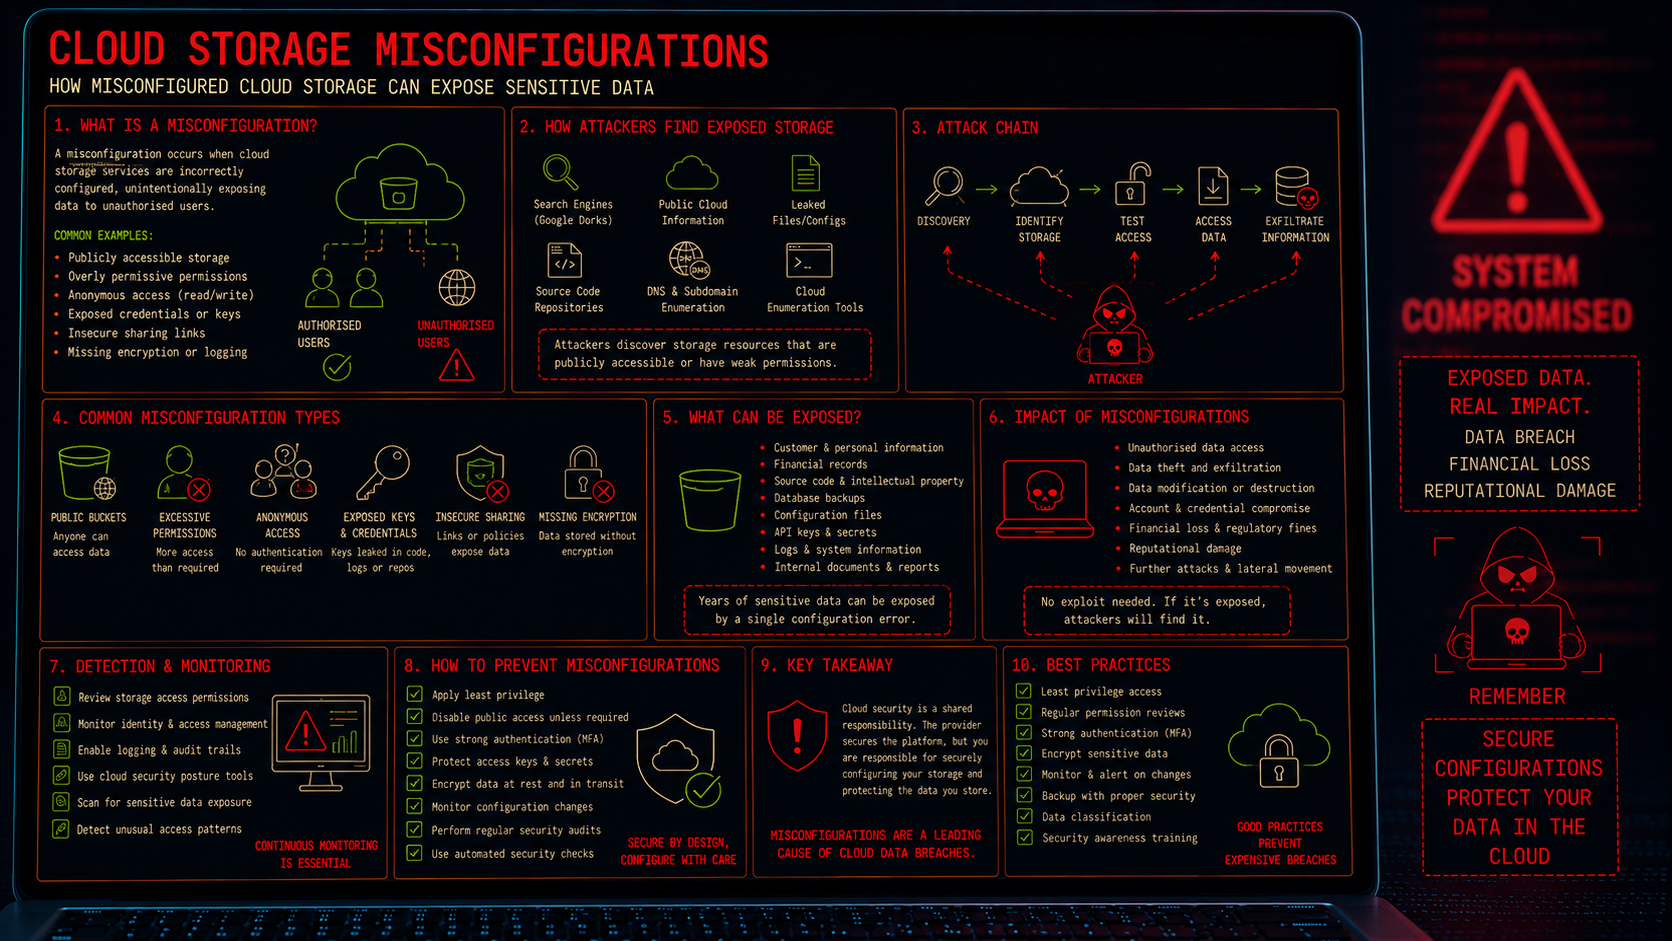 Cloud Storage Misconfigurations
Accidentally exposing data to the entire Internet
-
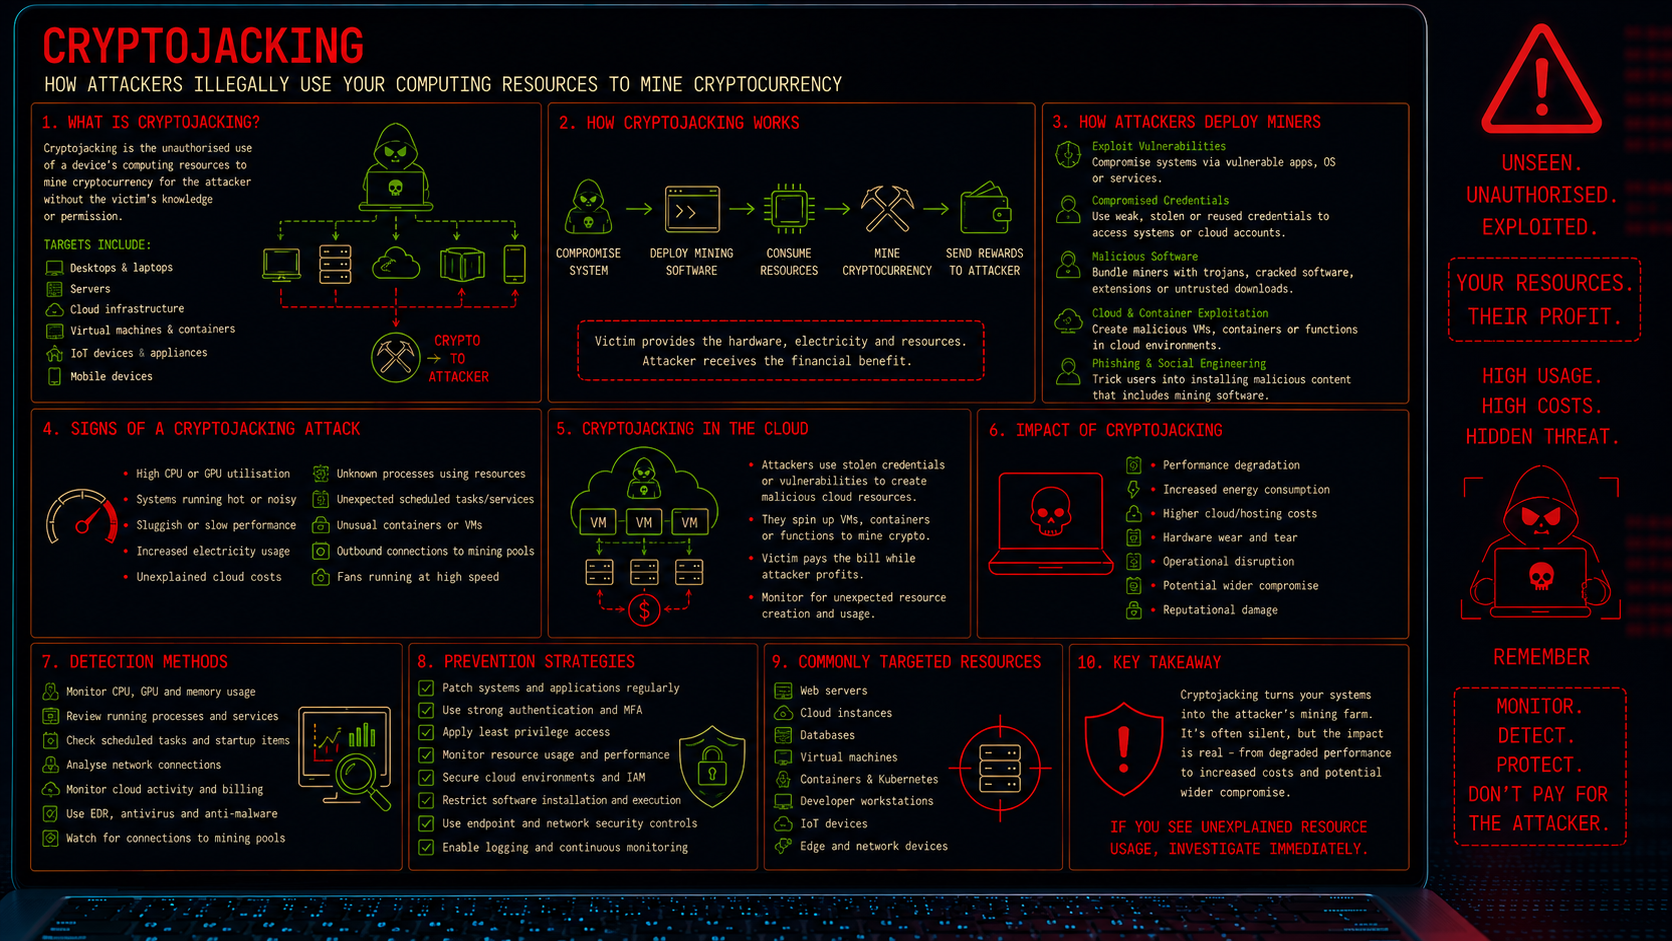 Cryptojacking
Utilising a victims infrastructure to generate illicit crypto-funds
-
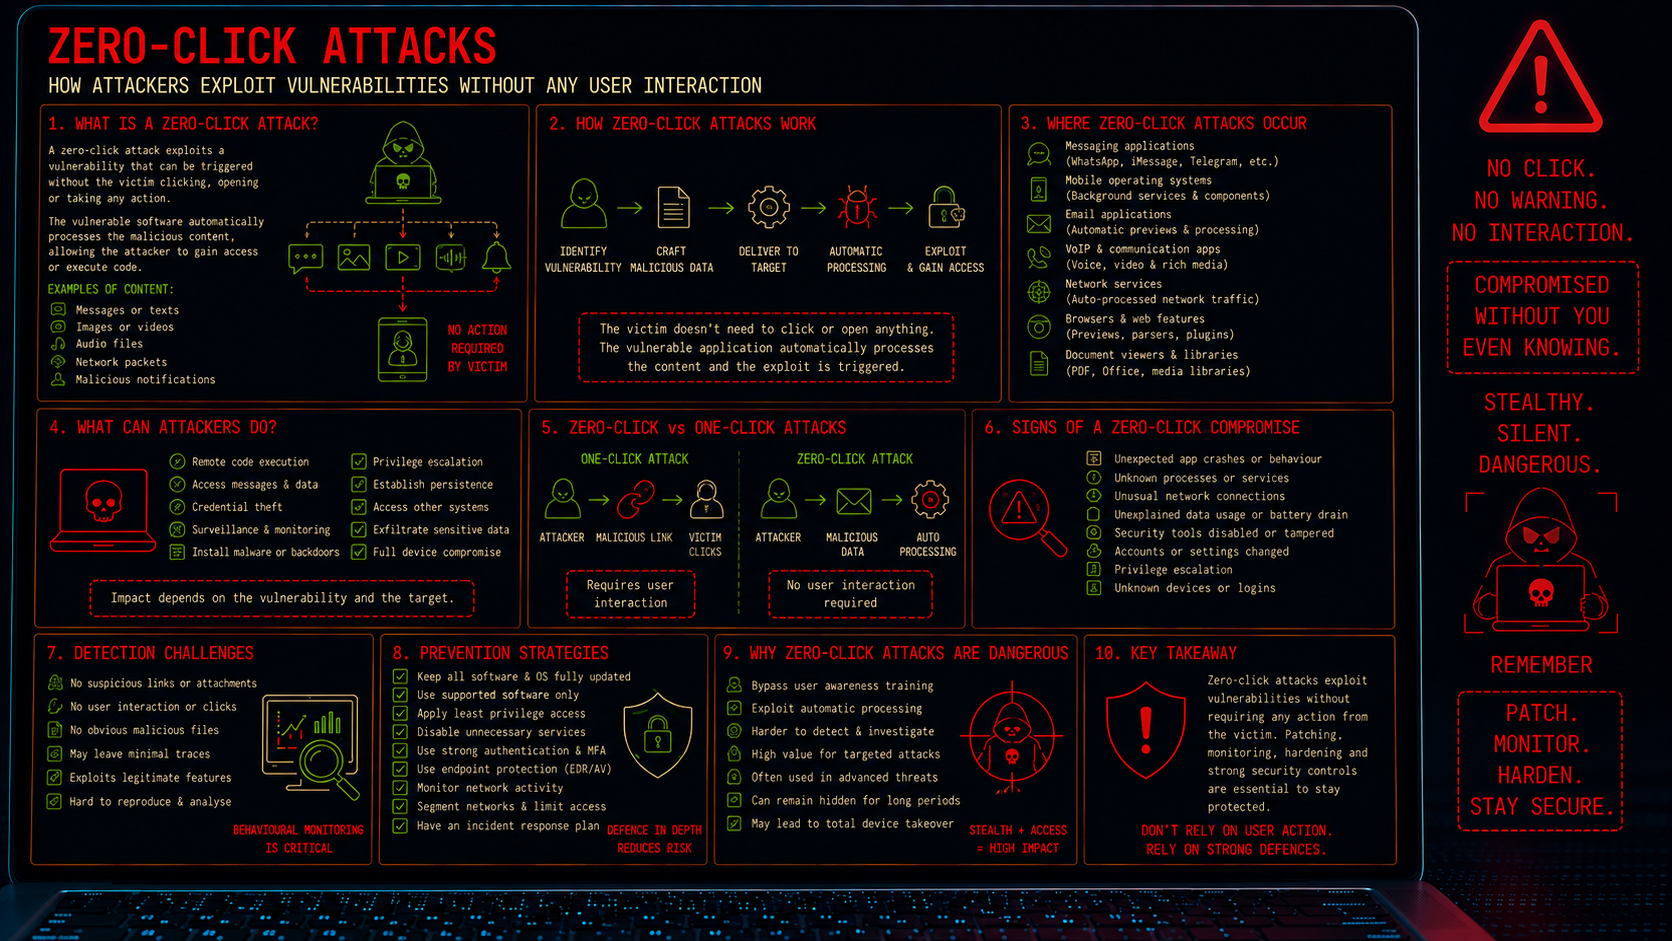 Zero-click attacks
Compromising accounts without any user interaction
-
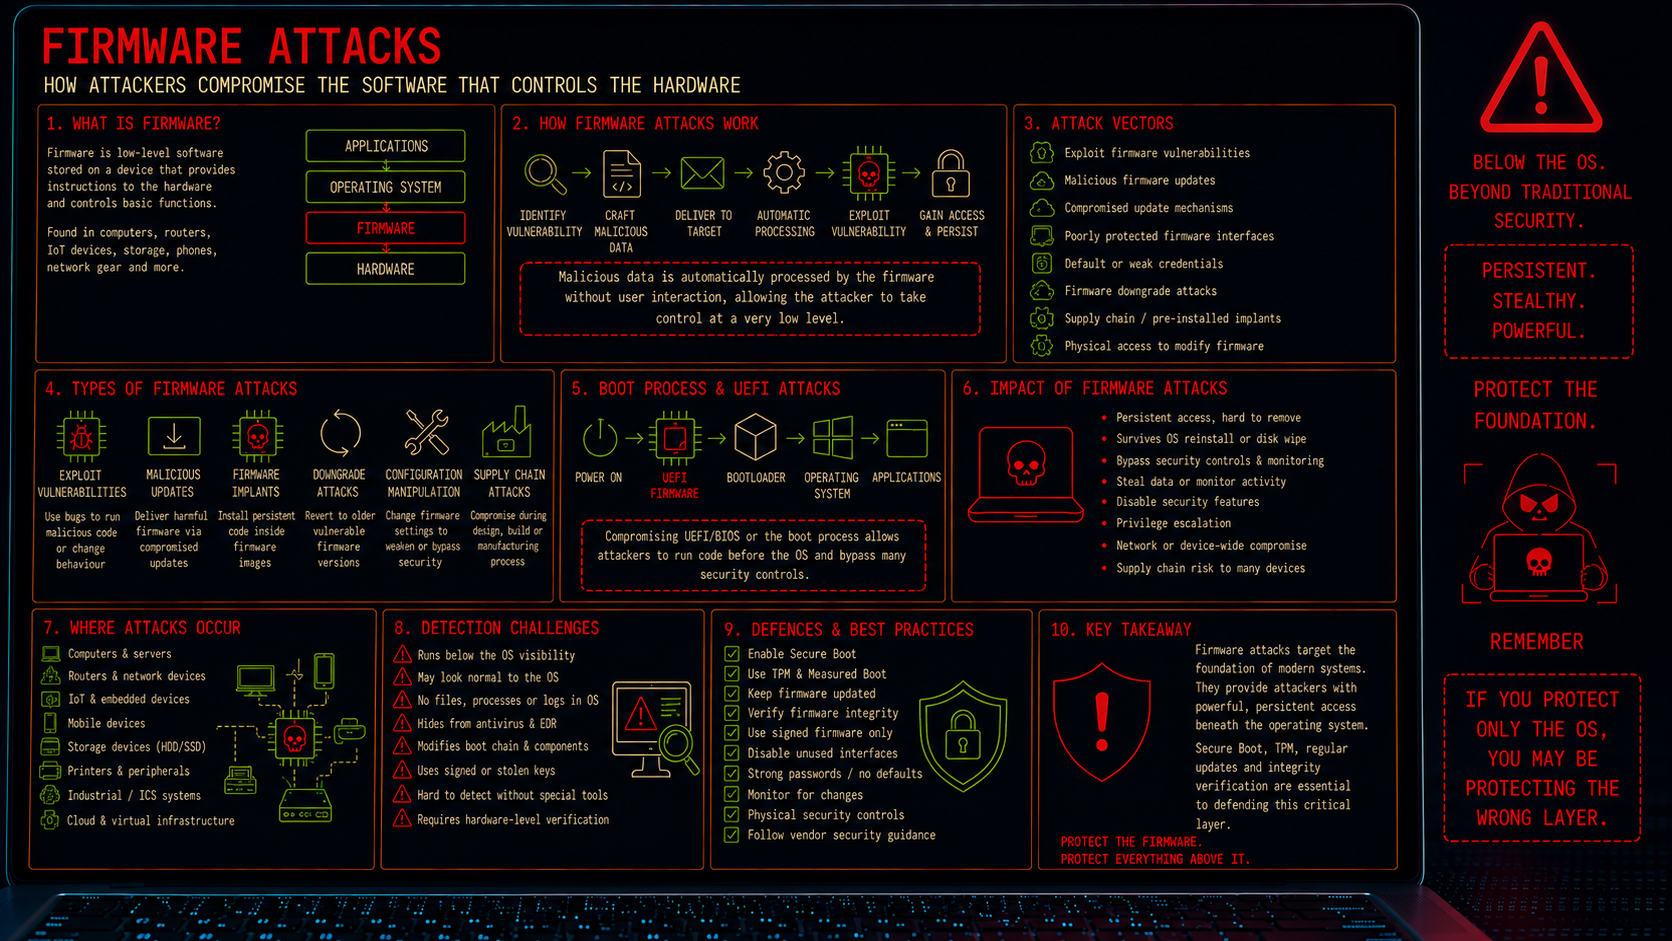 Firmware attacks
Compromising accounts without any user interaction
-
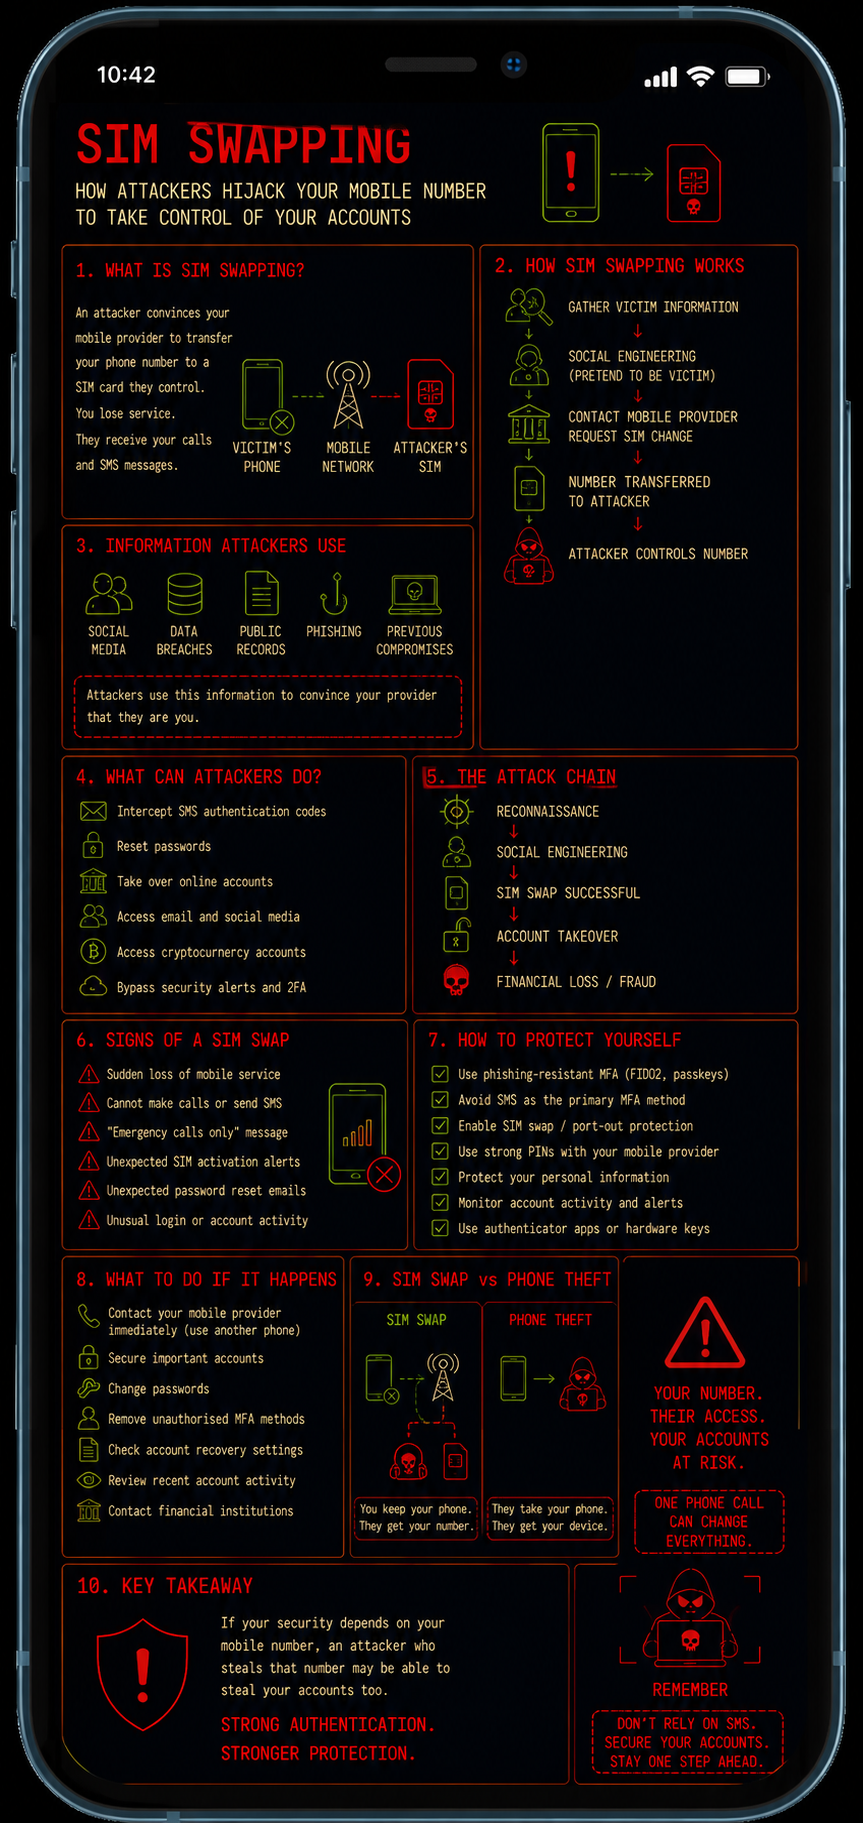 SIM swapping
Compromising accounts without any user interaction
-
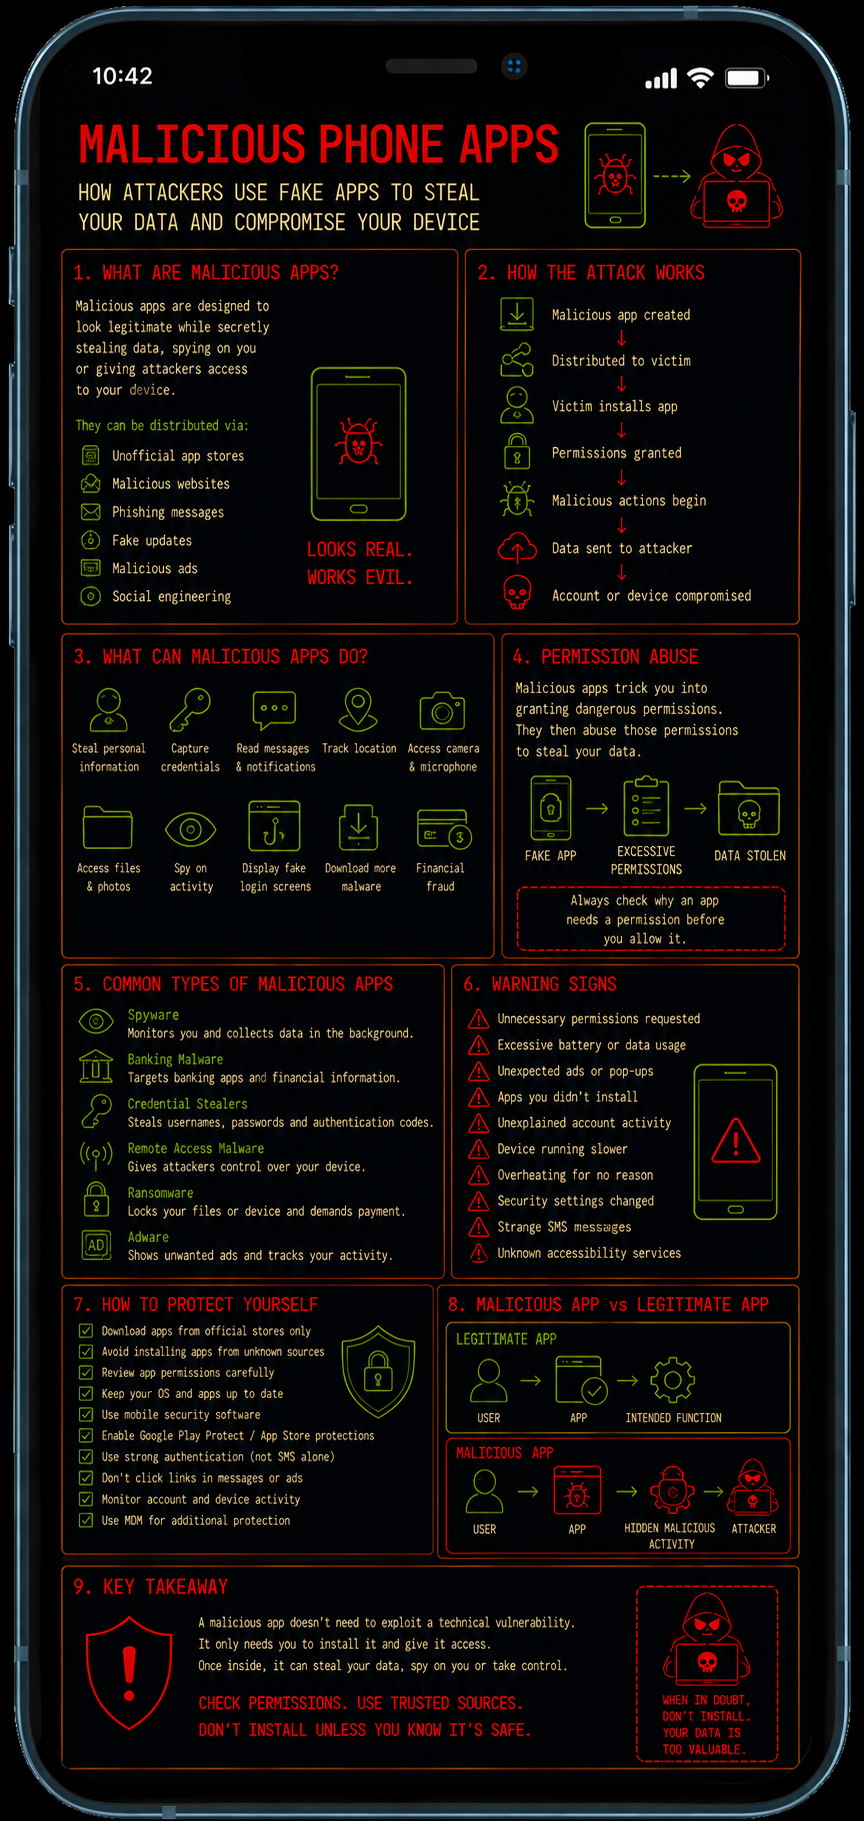 Malicious phone apps
Targeting users via games, utilities, updates, ads, and more
-
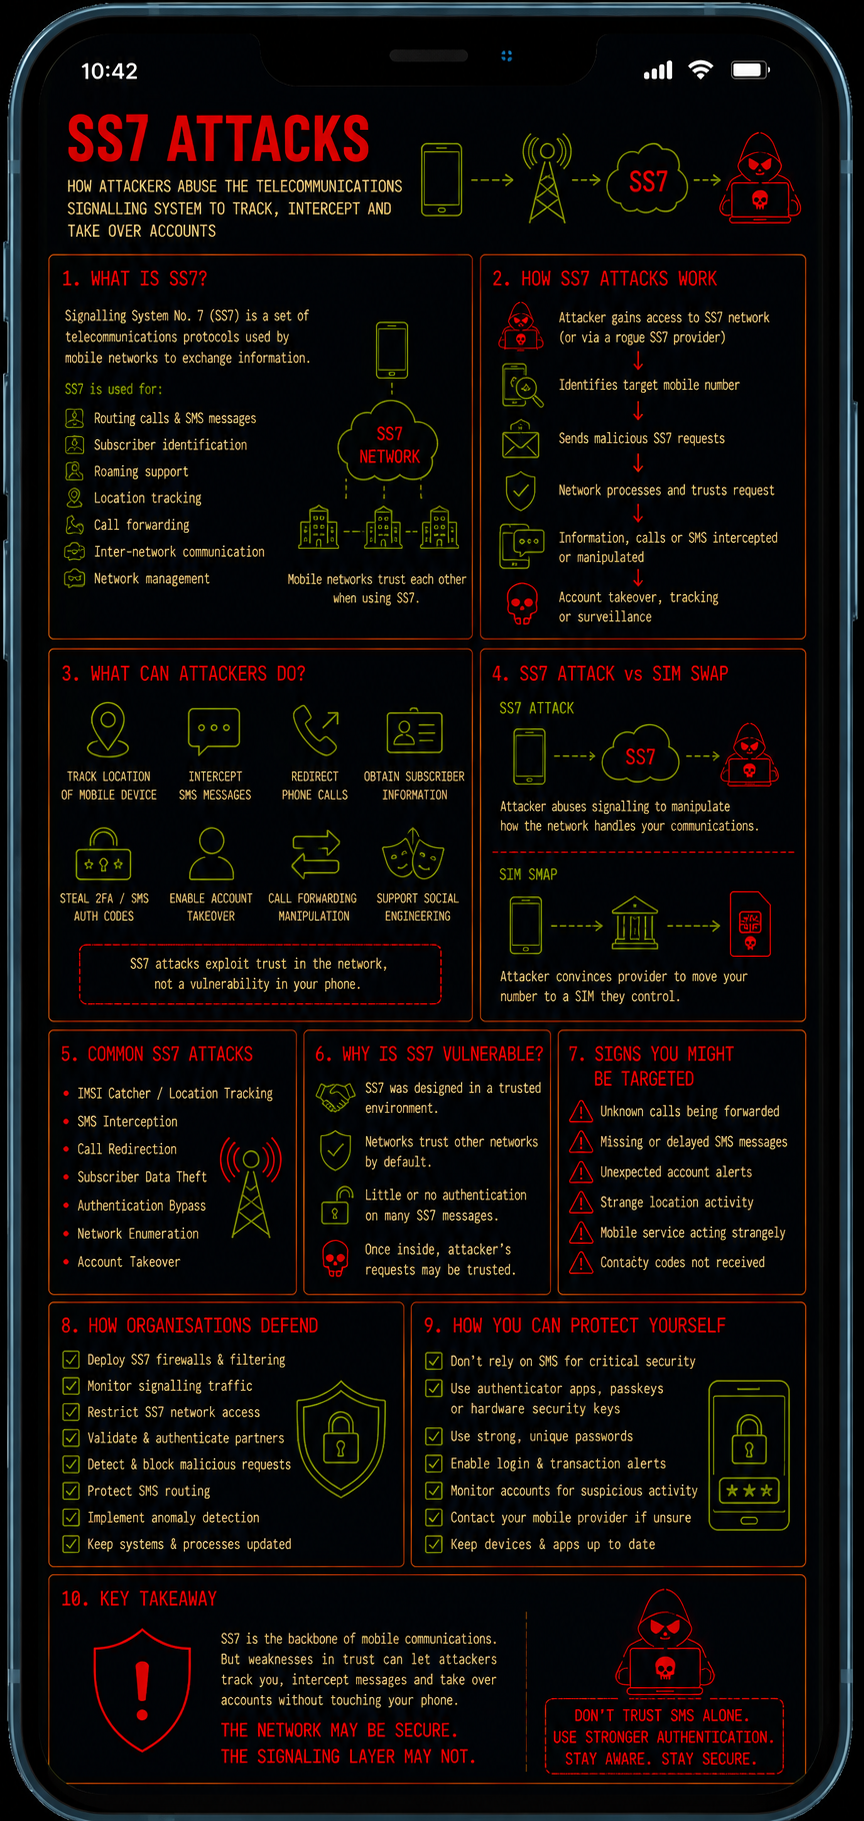
SS7 attacks
Attacking the mobile network to target users
-
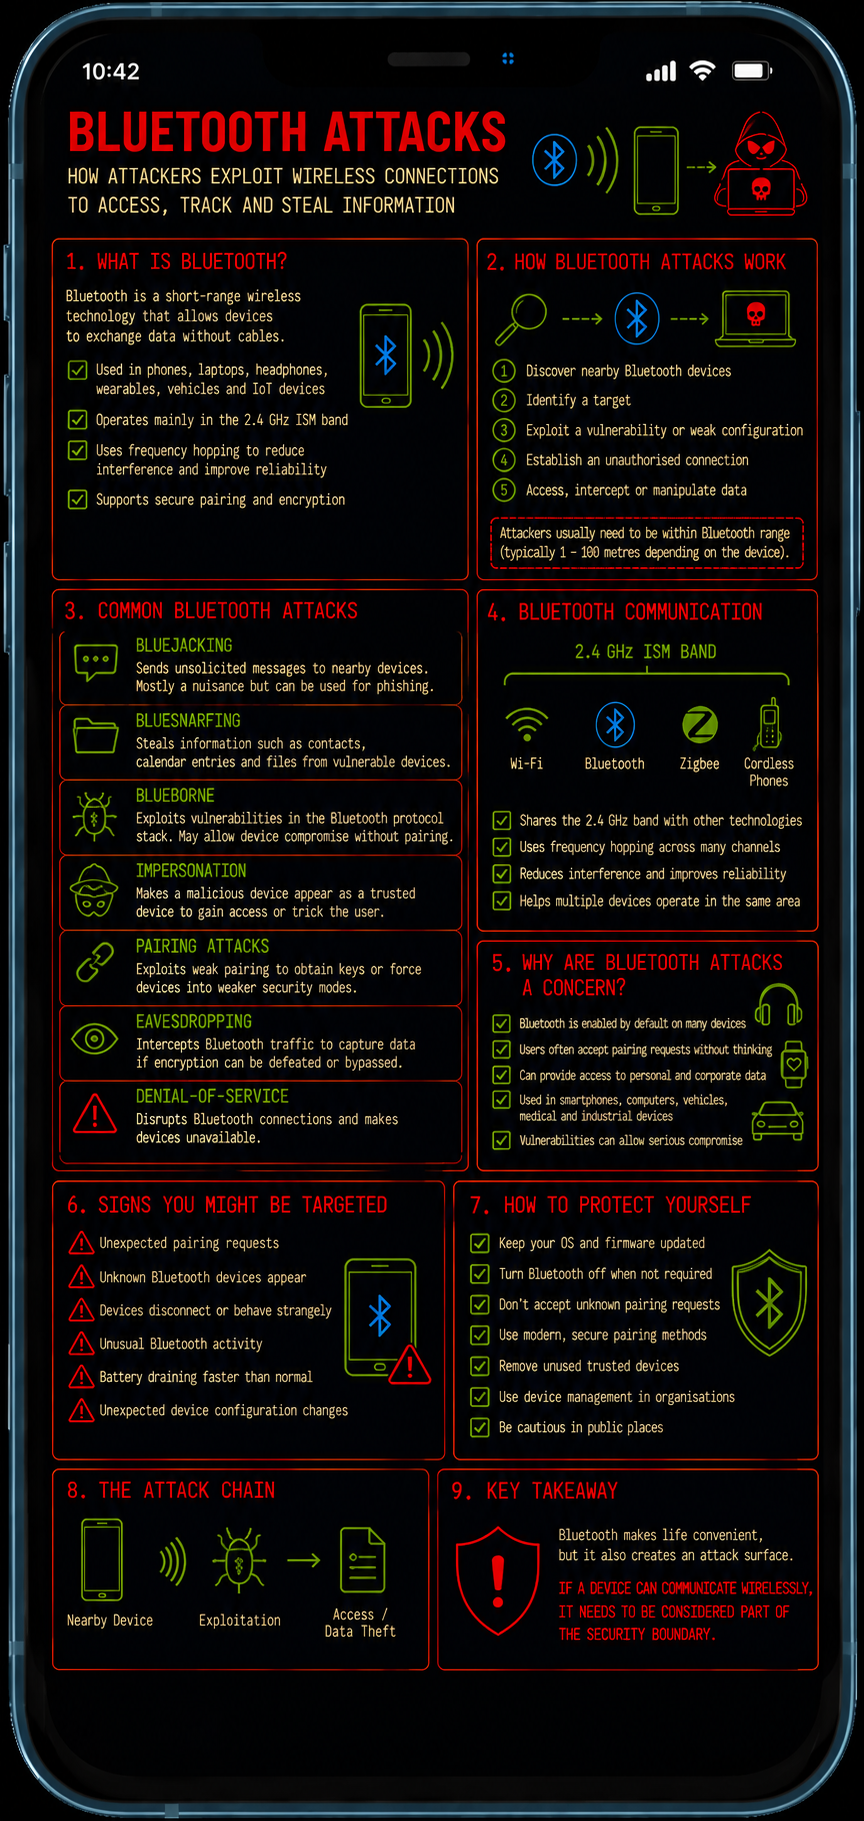
Bluetooth attacks
Targeting users via their wireless connections
-
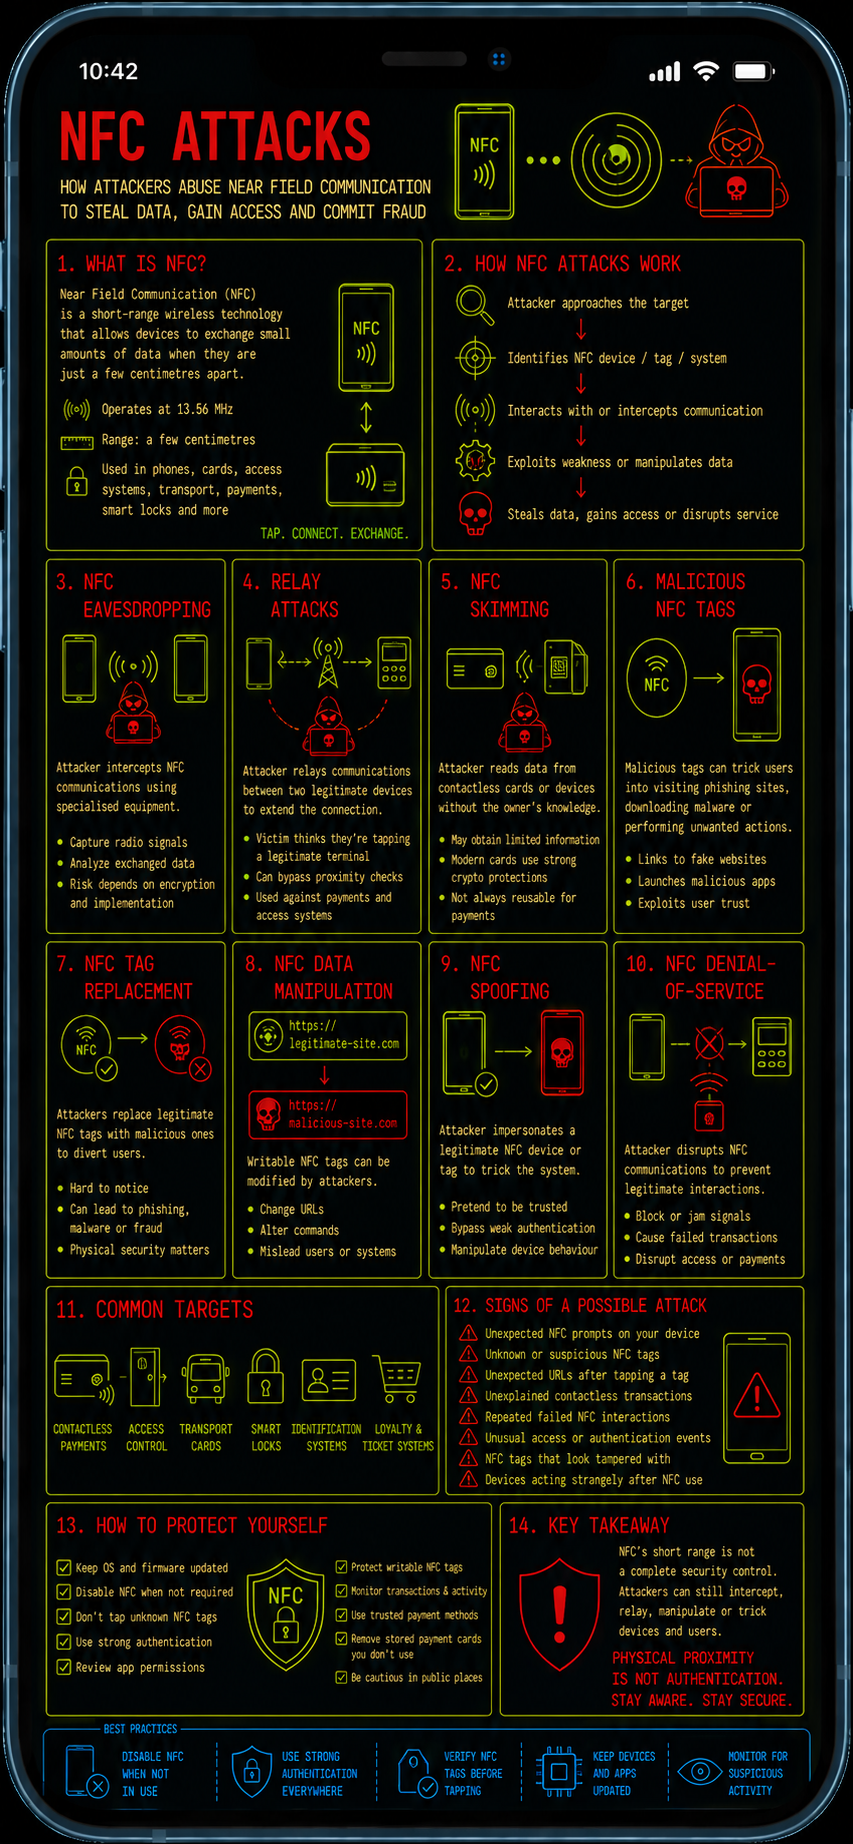
NFC attacks
Tap & Steal? Targeting users with short-range wireless attacks
-
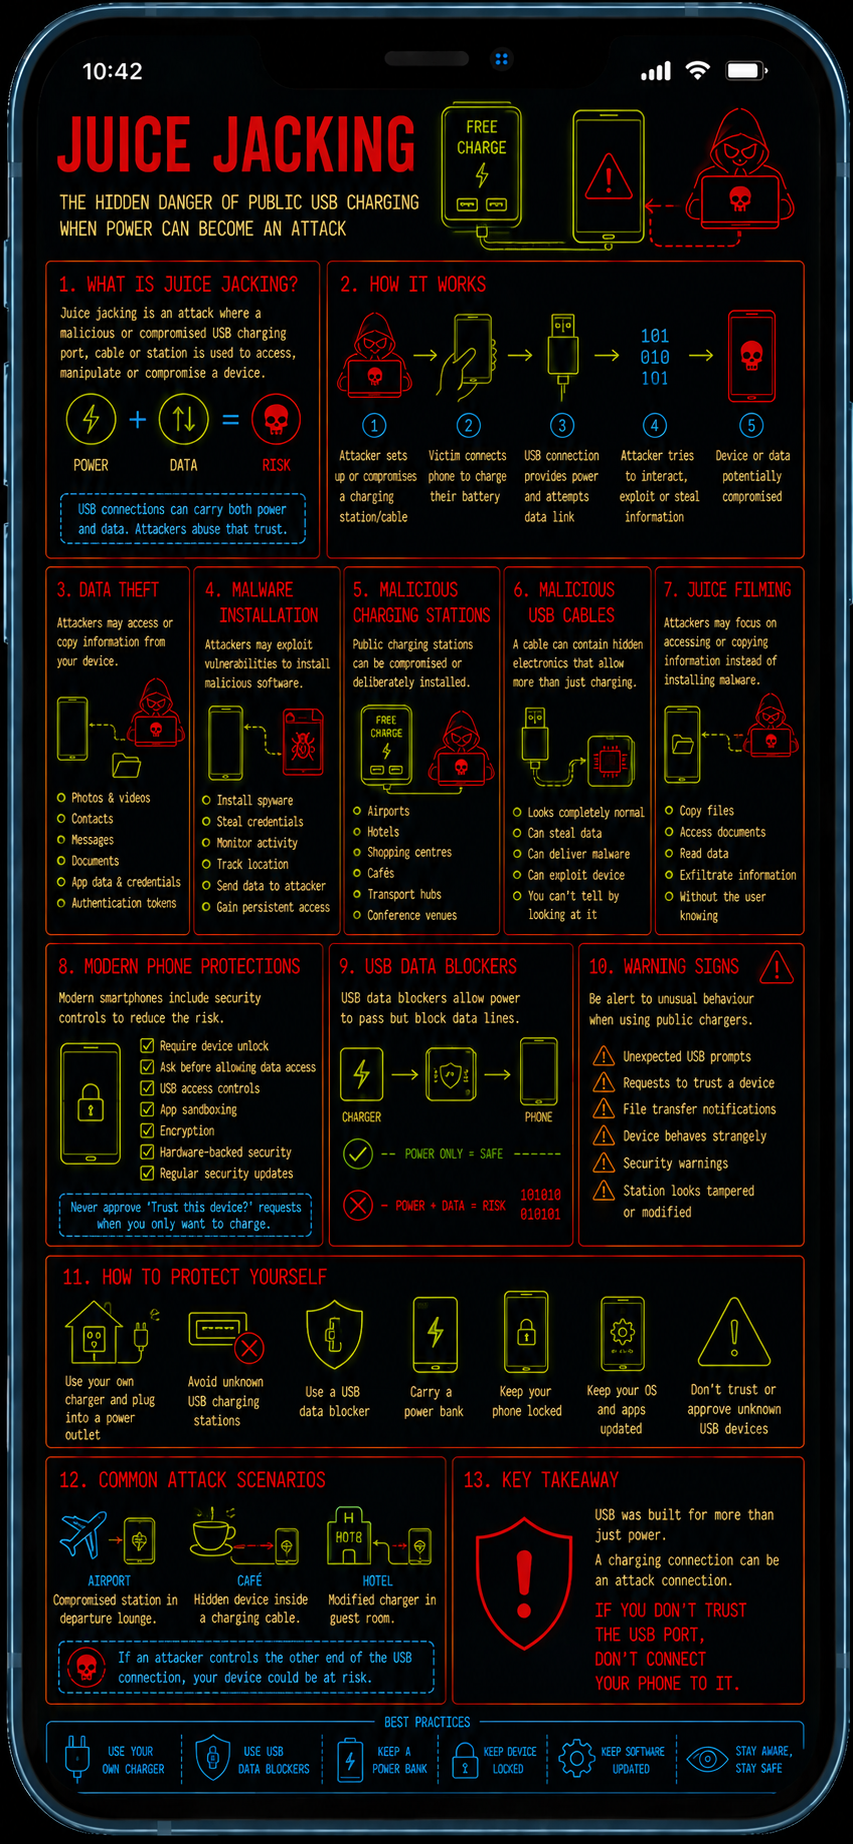 Juice Jacking
The hidden dangers of public USB charging
-
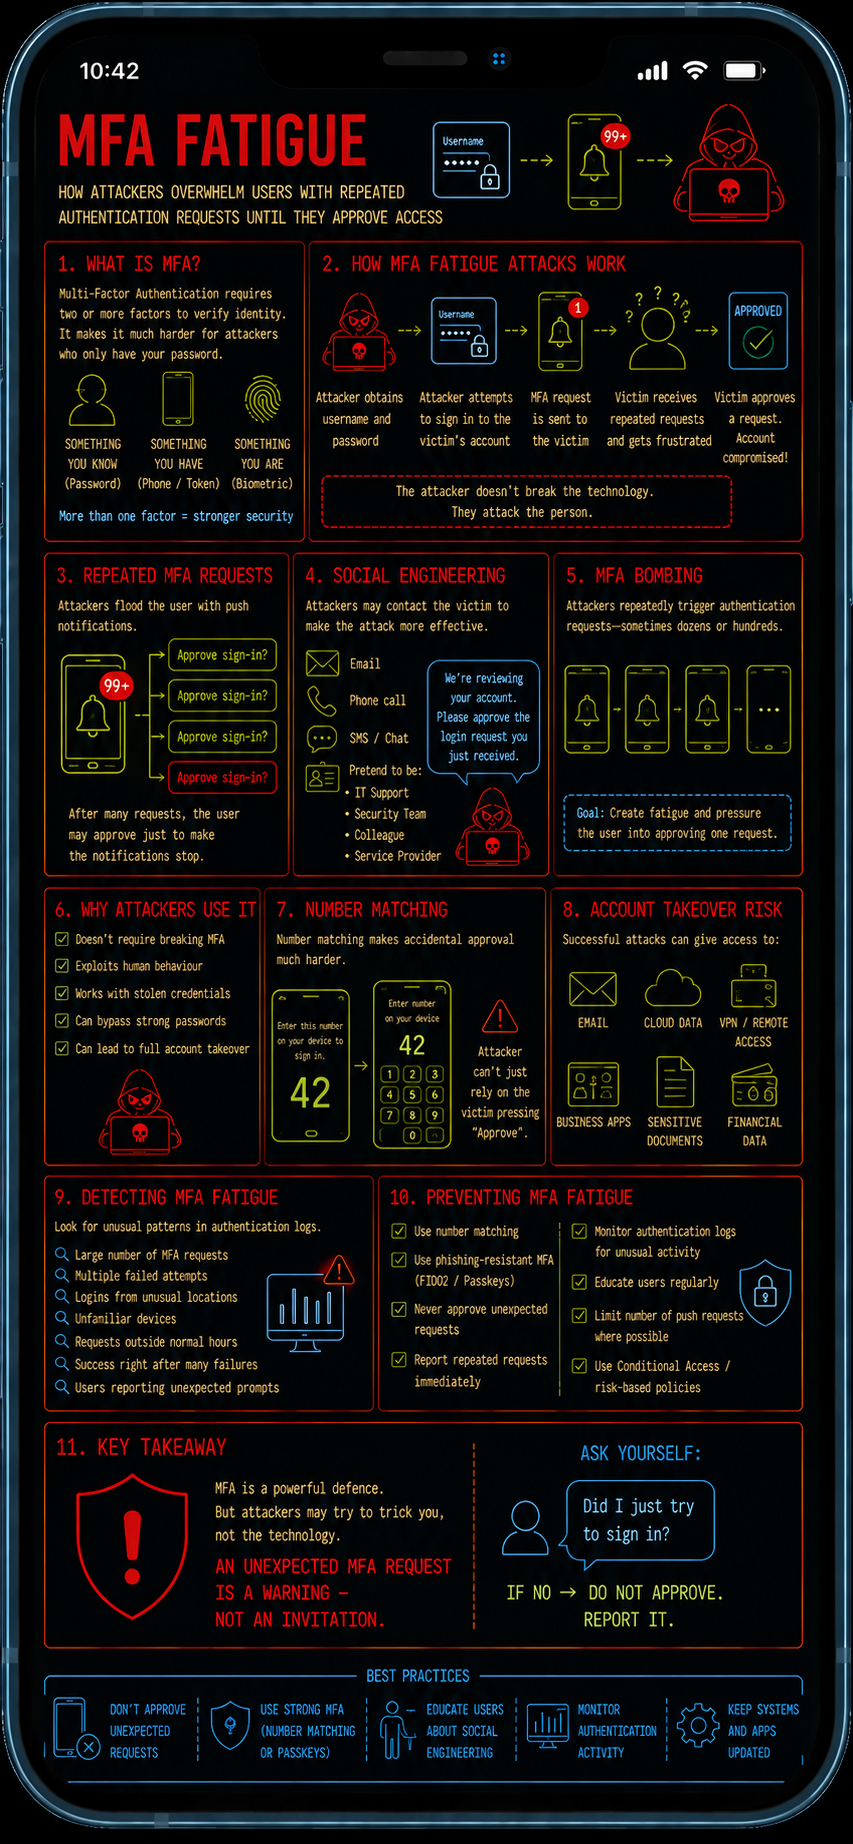 MFA fatigue
Faking authentication requests to trick users into granting access