
Understanding the attack designed to make systems unavailable
Introduction
Imagine trying to access a website, online banking service, gaming platform, or business application, only to find that it has suddenly stopped responding.
The server may still be running.
The network may still be connected.
The application itself may not have crashed.
Yet legitimate users cannot access it.
This is one of the primary objectives of a Distributed Denial of Service (DDoS) attack.
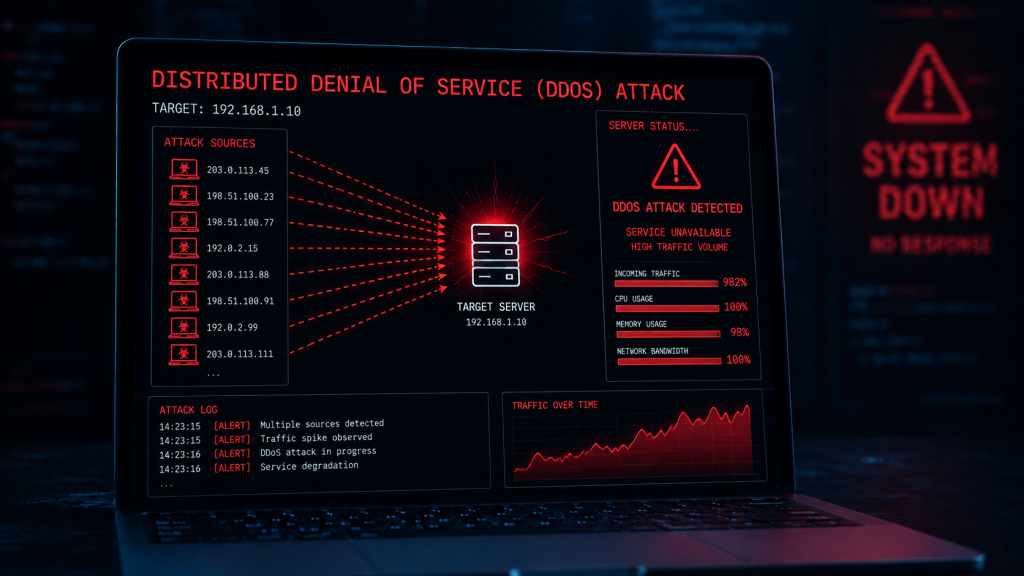
DDoS attacks are designed to overwhelm a target with enormous quantities of network traffic or malicious requests, consuming the resources required to provide a service to legitimate users.
The result can range from slow performance and intermittent connectivity to complete service disruption.
DDoS attacks have become an important part of the modern cyber threat landscape because attackers can increasingly launch large-scale attacks using networks of compromised computers, servers, Internet of Things (IoT) devices, and cloud infrastructure.
So, what is a DDoS attack?
DDoS stands for Distributed Denial of Service attack, and is an attempt to make a computer system, network, website, or online service unavailable by overwhelming it with traffic or requests from multiple sources. The word Distributed is particularly important.
A traditional Denial of Service (DoS) attack may originate from a single computer or connection, whereas a DDoS attack typically involves many different systems attacking the same target simultaneously.
This makes the attack:
- More difficult to block
- More difficult to trace
- Capable of generating significantly more traffic
- More difficult to distinguish from legitimate users
What is the difference between DoS and DDoS?
Although the terms are often used interchangeably, there is an important difference between the two types of attack.
Denial of Service
As mentioned, a DoS attack generally originates from a single source. So, for example:
An attacker sends a huge number of requests from one device to a web server. The server attempts to process those requests until its available resources are exhausted – During this time, legitimate users suffer the denial of the service.
Defending against an attack from one source is fairly trivial – simply blocking the IP address of the source system can be enough to prevent the success of the attack. In many cases, one device simply cannot generate enough traffic to overwhelm a modern system, so is inneffective anyway.
Distributed Denial of Service
A DDoS attack on the other hand uses multiple sources. The target is therefore dealing with traffic coming from many different IP addresses, which can change rapidly. Additionally, many devices working together can generate much more data to overload a victim system.
This makes DDoS attacks considerably more difficult to defend against.
How does a DDoS attack work?
A typical DDoS attack can be divided into several stages.
1. Building the attack infrastructure
The attacker first needs access to a large number of systems capable of generating traffic.
These systems may include:
- Compromised computers
- Servers
- Routers
- Internet of Things devices
- Security cameras
- Smart appliances
- Virtual machines
- Cloud infrastructure
The compromised systems collectively form what is termed a botnet.
2. Controlling the botnet
The attacker then needs a mechanism for controlling the compromised devices in the botnet. This may involve command-and-control infrastructure.
This infrastructure allows the attacker to issue instructions to the infected devices telling them when and where to send traffic.
The owners of the compromised devices in the botnet may have no idea that their equipment is participating in an attack as they only need to send small amounts of data to the target system, so performance of the device is not affected to an extent where it would be noticeable.
3. Selecting the target
The attacker identifies a target to attack, and the protocols to be used in the traffic sent to the target
The attacker may also specific services on the target that are likely to be vulnerable to large quantities of traffic.
4. Launching the attack
The attacker issues instructions to the botnet to begin sending traffic towards the target. Thousands or even millions of devices may participate in an attack.
The target is suddenly swamped with a huge increase in network traffic or application requests.
5. Exhausting resources
The target has a finite amount of:
- Network bandwidth
- CPU processing capacity
- Memory
- Connection capacity
- Application resources
- Firewall capacity
As these these resources become exhausted, legitimate users begin experiencing problems. Eventually, when all resources are consumed, legitimate users experience the full denial of service.
In severe cases, the underlying infrastructure may require intervention before normal service can be restored.
DDoS attacks as a form of extortion
DDoS attacks are commonly used for financial extortion. An attacker may threaten to launch a DDoS attack unless the victim pays money.
A often used tactic for cyber criminals is to use a DDoS attack as part of a ransomware campaign. Here DDoS attacks can act as a distraction while attackers conduct another operation elsewhere in the victim network.
This is particularly important for security teams, as DDoS attack should not automatically lead an organisation to assume that availability is the only issue. Security teams should investigate whether other suspicious activity is occurring at the same time.
How can organisations detect a DDoS attack?
One of the most obvious indicators of a DDoS attack is a sudden and unusual increase in traffic.
Security teams should monitor:
- Network bandwidth
- Packets per second
- Requests per second
- Connection rates
- Source IP addresses
- Geographic traffic patterns
- HTTP response times
- Server CPU utilisation
- Memory utilisation
- Firewall logs
- Load-balancer statistics
However, detecting a DDoS attack is not always straightforward. A sophisticated application-layer DDoS attack can generate traffic that looks remarkably similar to legitimate users.
For this reason, organisations often combine multiple indicators rather than relying on traffic volume alone.
Signs of a DDoS attack
Common warning signs include:
- Sudden unexplained traffic spikes
- Website performance becoming extremely slow
- Large numbers of failed connections
- Unusual traffic from particular regions
- Large numbers of requests for the same resource
- High CPU or memory usage
- Network bandwidth reaching capacity
- Firewalls or load balancers becoming overloaded
- Legitimate users reporting connection problems
A sudden increase in traffic does not automatically mean a DDoS attack. A legitimate event, such as a successful marketing campaign or major news story, can also generate unusually high traffic.
Security teams therefore need to distinguish between a traffic spike and a malicious traffic flood.
How organisations defend against DDoS attacks
DDoS protection generally relies on multiple layers of defence.
Traffic filtering
Firewalls and filtering systems can identify and block malicious traffic.
Filtering may be based on:
- Source addresses
- Protocols
- Ports
- Traffic patterns
- Request characteristics
However, filtering alone may not be sufficient when the attack is extremely large.
Rate limiting
Rate limiting restricts how many requests a client can make within a specific period.
For example, a service might limit the number of requests a single client can make.
This can reduce the effectiveness of application-layer attacks.
Load balancing
Load balancers distribute traffic across multiple servers.
This can prevent a single server from becoming overwhelmed.
However, load balancing does not necessarily solve the underlying problem if the total volume of malicious traffic exceeds the available infrastructure.
Content Delivery Networks
A Content Delivery Network (CDN) distributes content across multiple geographically distributed servers.
This can help absorb and distribute large volumes of traffic.
Many modern organisations use CDN providers that include dedicated DDoS protection.
DDoS mitigation services
Specialised DDoS protection services can identify malicious traffic and filter it before it reaches the organisation’s infrastructure.
Traffic may be routed through a mitigation provider where malicious requests are removed while legitimate traffic is allowed through.
Redundancy
Organisations can design their infrastructure with redundancy.
This may include:
- Multiple servers
- Multiple network connections
- Multiple data centres
- Geographic distribution
- Cloud-based infrastructure
The objective is to ensure that failure or overload in one location does not result in complete service loss.
How individuals can protect themselves
Individuals are less likely to be the target of large-scale DDoS campaigns, but their devices are targeted in attempts to subvert them into a botnet.
Good security practices to prevent this from happening include:
- Keep operating systems updated.
- Keep routers and IoT devices updated.
- Change default passwords.
- Use strong, unique passwords.
- Enable multi-factor authentication where available.
- Disable unnecessary Internet-facing services.
- Avoid exposing administrative interfaces directly to the Internet.
- Replace unsupported or obsolete devices.
These measures can reduce the likelihood that personal devices will be compromised and used in attacks against other organisations.
DDoS attacks and IoT devices
The rapid growth of Internet-connected devices has created a huge potential attack surface.
Many IoT devices are:
- Permanently connected
- Rarely monitored
- Difficult to update
- Protected by weak credentials
- Exposed directly to the Internet
This makes them attractive targets for botnet operators.
Once compromised, an IoT device may continue operating normally from the perspective of its owner while secretly participating in DDoS attacks.
This makes IoT security an important part of modern DDoS defence.
The future of DDoS attacks
DDoS attacks continue to evolve alongside Internet infrastructure. Several developments are particularly important.
- Larger attack infrastructure
The number of Internet-connected devices continues to increase. This provides attackers with an enormous potential pool of systems that could potentially be compromised and incorporated into botnets. - Cloud-based attacks
Cloud infrastructure provides attackers with access to highly scalable computing and networking resources. This creates new opportunities for attackers while simultaneously providing defenders with additional tools for absorbing malicious traffic. - Application-layer attacks
As organisations improve their ability to defend against simple volumetric attacks, attackers increasingly have incentives to target applications directly. Application-layer attacks can be more difficult to distinguish from legitimate activity. - AI and automation
Artificial intelligence and automation could potentially make attacks more adaptive. For example, automated systems could analyse responses from a target and modify attack traffic accordingly. At the same time, defenders can use automation and machine learning to identify unusual traffic patterns and respond more quickly.
The future of DDoS defence is therefore likely to involve increasingly automated detection and mitigation.
Conclusion
Lost revenue, reputational damage, customer dissatisfaction, operational disruption, and the potential use of DDoS attacks alongside other forms of cybercrime make them an important threat for modern organisations.
Understanding how DDoS attacks work is therefore an essential part of cybersecurity knowledge.
The objective is not simply to understand how attackers generate large amounts of traffic. It is to understand how availability can be attacked, how those attacks can be detected, and how resilient systems can be designed to withstand them.