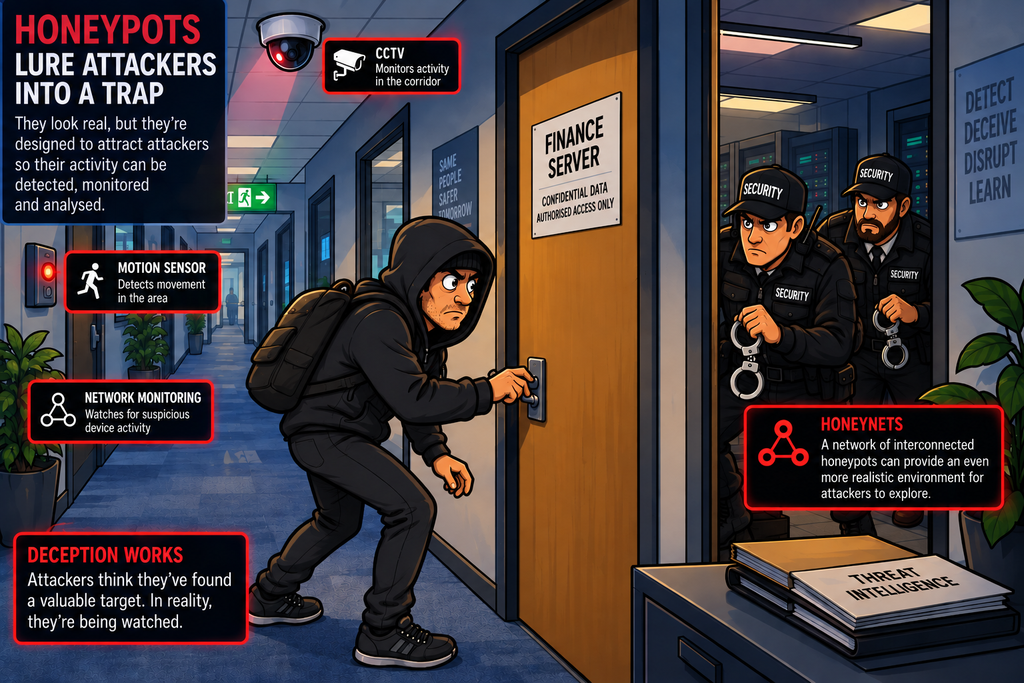
Imagine a burglar breaking into a building – They find what appears to be a room containing valuable equipment and documents. It looks like an easy target.
But there is a problem.
The room was deliberately created to look attractive to burglars.
The doors are monitored. The equipment is being watched. Every movement is recorded.
The burglar hasn’t found the organisation’s real assets.
They have walked into a trap.
This is the basic idea behind a honeypot.
A honeypot is a deliberately deployed system, service or resource designed to attract attackers so that their activity can be detected, monitored and analysed.
A collection of interconnected honeypots and other deceptive systems is known as a honeynet.
A honeypot gives attackers something to attack. A honeynet creates an entire environment for them to explore.
They are primarily detective security controls, but they can also provide valuable intelligence about attackers and their techniques.
What Is a Honeypot?
A honeypot is a system or resource deliberately designed to attract unauthorised activity.
It might look like:
- A server
- A database
- A file share
- A web application
- An administrator account
- An IoT device
- A network service
- A workstation
The key characteristic is that the resource is not there because the organisation actually needs attackers to access it – It exists to provide visibility into malicious activity.
Why Use a Honeypot?
A honeypot can provide a very useful security signal.
Imagine an organisation has a server called SERVER-01.
This server exists so that employees can legitimately use it.
Now imagine another server called SERVER-99
This server appears to contain interesting information but isn’t used by legitimate employees.
If someone starts accessing SERVER-99 – That activity is immediately interesting.
The Important Principle
A honeypot works partly because there should be very little legitimate activity on it, so any activity seen on it should arouse suspicion.
This can make honeypot alerts particularly valuable from a detection perspective.
A Honeypot Is Not Just a Fake Server
A honeypot doesn’t necessarily have to be a complete physical or virtual computer.
It could be something as simple as a fake file share, web app, user account, or set of credentials
The objective is to create something that an attacker is likely to interact with.
What Is a Honeynet?
A honeynet takes the idea of a honeypot and expands it into a network of interconnected systems. This looks more realistic, so is likely to attract more interest, but also, it allows for analysts to see more of the attackers way of working.
The attacker may be able to move between several systems. This gives defenders much more information about what the attacker is attempting to do, so they can look for evidence of the same activity in the real network.
The distinction between the two systems is straightforward.
A Honeypot is a single deceptive resource.
A Honeynet is a collection of deceptive systems forming an environment.
Why Would an Attacker Attack a Honeypot?
A honeypot needs to look sufficiently interesting to attract attention.
It might appear to contain:
- Customer Database
- Financial Records
- Administrator Portal
- Source Code
- Backup Server
- Internal Documents
An attacker looking for valuable targets may decide to investigate it.
The objective isn’t necessarily to make the honeypot obviously vulnerable – It needs to look plausible or the attacker might smell a rat and avoid it.
Honeypots are part of a broader security concept called deception – Instead of simply trying to keep attackers away, the organisation deliberately presents them with misleading targets.
Honeypots are sometimes described as decoy systems – ones designed to look sufficiently realistic that an attacker will interact with it, but legitimate users should have no reason to interact with it.
A particularly interesting type of deception is the use of decoy credentials.
For example, an organisation might create: a decoy backup-admin account
The account might appear to be useful, but it shouldn’t provide access to genuine sensitive systems.
If someone attempts to use those credentials however, it should immediately flag in the system.
These are sometimes referred to as honeytokens.
Examples of honeytokens include:
- Fake credentials
- Fake API keys
- Fake database records
- Fake documents
- Fake email addresses
- Fake URLs
The key doesn’t necessarily need to provide access to anything valuable – Its purpose is to reveal that someone has obtained and attempted to use it.
A useful distinction is:
| Technology | What it is |
|---|---|
| Honeypot | A deceptive system or service |
| Honeynet | A network of deceptive systems |
| Honeytoken | A deceptive piece of information or digital resource |
All three are forms of security deception.
Honeypots and Reconnaissance
Honeypots can also help detect reconnaissance.
Attackers regularly scan networks looking for interesting systems.
Because legitimate users have no reason to scan the honeypot, the event can be highly suspicious.
A honeypot can expose services that appear interesting.
For example, it may host services such as SSH or RDP which attackers could abuse to gain access to the network
An attacker scanning the system may discover these ports and begin investigating.
The honeypot can record the activity.
A fake SSH service might also attract password guessing, or password spraying
The system can record:
- Source address
- Usernames attempted
- Password patterns
- Timing
- Commands attempted
This can provide useful intelligence.
Honeypots and Malware
A honeypot can also be used to study malware behaviour.
By placing vulnerable services in the honeypot, security researchers can analyse what the malware attempts to do and then use this data to update antimalware defences, etc.
High-Interaction Honeypots
Honeypots can differ in how realistic they are.
A high-interaction honeypot provides a more complete environment for an attacker to interact with.
For example it may contain a fully-featured operating system, with typical end-user applications (productivity suites, graphics packages, collaboration tools, development tools, etc.) It could also contain realistic-looking work documents, and also have other network capabilities such as VPN software, etc.
The attacker may be able to perform many actions with these services and files that will produce much richer intelligence.
Low-Interaction Honeypots
A low-interaction honeypot provides a more limited simulation.
The attacker doesn’t receive a complete operating environment, but it still provides an interesting opportunity for the attacker
There is a trade-off between the different types of honeypot.
| Type | Advantages | Disadvantages |
|---|---|---|
| Low interaction | Easier and safer to operate | Less realistic information |
| High interaction | Richer attacker behaviour | More complex and potentially riskier |
The appropriate choice depends on the purpose of the honeypot.
Production Honeypots
A honeypot doesn’t necessarily need to be completely separate from the production environment. An organisation might place carefully controlled decoys inside its real network.
An attacker who has already gained internal access may encounter the decoy while exploring the network.
This can make honeypots particularly useful for detecting lateral movement.
Suppose an attacker compromises one workstation.
Using the access and trust of that workstation, they begin looking for other systems
If the attacker interacts with a system that no legitimate user should access, the security team gets a valuable signal.
The honeypot provides another opportunity to identify the attacker. This is a good example of Defence in Depth.
Honeypots and EUBA
Honeypots can work well with Entity and User Behaviour Analytics (EUBA).
Suppose a user normally behaves like this:
User
 │
 ├── Email
 ├── CRM
 ├── Sales files
 └── Collaboration tools
Suddenly:
User
 │
 ├── Accesses decoy server
 ├── Uses unusual account
 ├── Scans network
 └── Attempts sensitive file access
EUBA can combine these unusual behaviours into a higher-risk assessment.
Honeypots and SIEM & SOAR
Honeypots produce useful security events which should be sent to a SIEM for analysis.
The SIEM can then correlate the honeypot activity with other events.
Honeypot alerts can also trigger automated workflows using SOAR.
Depending on the organisation’s response procedures, automated actions might include:
- Blocking an IP address
- Isolating a device
- Disabling an account
- Creating an incident
- Collecting additional evidence
A Compromised Honeypot Is Still a Compromised System
This is an important point.
A honeypot is deliberately designed to attract attackers – That means it may eventually be compromised.
The security team must therefore treat it as a potentially hostile system. It should not be trusted simply because it is a security tool.
Don’t Put Real Sensitive Data in a Honeypot
A honeypot should not normally contain genuine sensitive information simply to make it look realistic.
Instead, it can use:
- Synthetic data
- Fake credentials
- Decoy documents
- Simulated databases
- Controlled services
The objective is to make the environment attractive without unnecessarily exposing real information.
Honeypots and Legal Considerations
Organisations need to consider legal and ethical issues when deploying honeypots.
For example:
- What data is collected?
- Is personal information captured?
- How long is it retained?
- Who can access it?
- Can activity be shared with third parties?
- Does monitoring cross organisational boundaries?
Honeypots should therefore be designed and operated within appropriate organisational policies and legal requirements.
Honeypots Can Provide Threat Intelligence
As mentioned. one of the most valuable uses of honeypots is learning about attackers.
They can reveal:
- Attack techniques
- Tools
- Commands
- Malware
- Usernames
- Password patterns
- Source infrastructure
- Exploitation attempts
- Lateral-movement techniques
This information can then improve other security controls.
Honeypots and Attack Research
As well as being used by organisations, honeypots are commonly set up by security teams and researchers to study:
- Automated attacks
- Botnets
- Malware campaigns
- Credential attacks
- Network scanning
- Exploitation techniques
Because the environment is deliberately controlled, researchers can observe activity without putting genuine production systems at unnecessary risk.
Automated Attackers
Not every attacker interacting with a honeypot is a human.
The Internet is constantly scanned by:
- Bots
- Worms
- Automated scanners
- Malware
- Criminal infrastructure
A honeypot can attract this automated activity which can provide useful information about threats affecting the wider Internet.
Honeypots can also help identify ransomware activity.
For example, an organisation might create decoy files used to attract ransomware attacks
If malware suddenly modifies or encrypts those files, the way the ransomware operates can be carefully scrutinised to identify any way of reversing the encryption.
These are sometimes referred to as honeyfiles or can form part of a broader deception strategy.
The Limitations of Honeypots
Honeypots are useful, but they have limitations.
They cannot:
- Detect every attack
- Protect every real system
- Replace firewalls
- Replace EDR
- Replace access controls
- Replace patch management
- Guarantee that attackers will interact with them
An attacker may simply never encounter the deception.
Attackers Can Detect Honeypots
Sophisticated attackers may try to determine whether a system is a honeypot.
Attackers can sometimes fingerprint systems to determine what they are dealing with.
They might look for:
- Unusual system configurations
- Missing applications
- Unrealistic data
- Virtualisation clues
- Network characteristics
- Unusual responses
- Monitoring software
If they recognise the deception, then the honeypot provides little intelligence about that attacker.
In Summary
A honeypot is a deliberately deployed deceptive system or resource designed to attract attackers and detect or study their activity.
A honeynet is a collection of interconnected honeypots that provides a larger deceptive environment.
Related deception technologies include:
- Honeypots – Fake systems or services designed to attract attackers.
- Honeynets – Networks containing multiple deceptive systems.
- Honeytokens – Fake credentials, keys or other information that trigger an alert when used.
- Honeyfiles – Decoy documents or files designed to detect unauthorised access.
Honeypots can help detect:
- Reconnaissance
- Port scanning
- Brute-force attacks
- Malware
- Lateral movement
- Privilege escalation
- Insider threats
- Credential misuse
- Data theft
- Ransomware activity
They work particularly well alongside:
- Logging and Auditing
- SIEM
- SOAR
- EUBA
- EDR
- IDS/IPS
- Network Segmentation
- Access Controls
- Defence in Depth
- Incident Response
The most important thing to remember is that a honeypot isn’t primarily there to stop an attacker – It’s there to make the attacker’s behaviour visible.
That makes honeypots a particularly interesting detective control.
Don’t just defend your real systems. Sometimes, give the attacker a convincing fake one – and watch what they do.